Themata.AI
Themata.AI

Popular tags:

#developer-tools#ai-agents#discussion#trending#llms#ai-ethics#claude#code-generation#ai-safety#openai

AI is changing the world. Don't stay behind. Clear summaries, community insight, delivered without the noise. Subscribe to never miss a beat.

© 2026 Themata.AI • All Rights Reserved

Archive

|

Topics

|

Privacy

|

Cookies

|

Contact
🕒 Latest🔥 Top

Filtering by tag:

code-executionClear
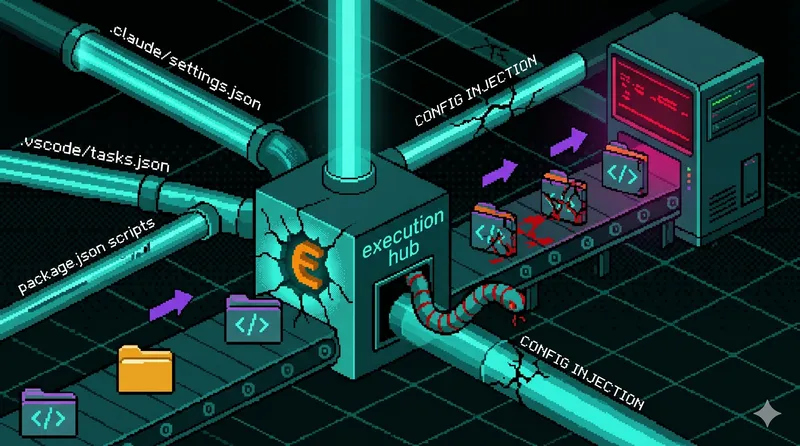
Config Files That Run Code: Supply Chain Security Blindspot
supply-chain-securitydeveloper-toolsai-agentscode-execution
Research

Config Files That Run Code: Supply Chain Security Blindspot

Config files in repositories can execute code automatically when opened by development tools, potentially allowing attackers to run malicious code without the developer's awareness. Tools such as VS Code, Cursor, Claude Code, Gemini CLI, npm, Composer, and Bundler can read and act on these config files.

safedep.io

🔥🔥🔥🔥🔥

10 min

6/8/2026

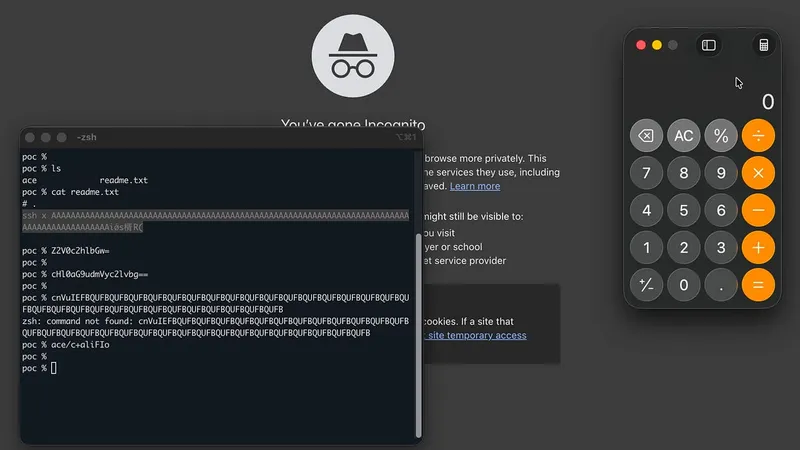
Even "cat readme.txt" is not safe

Using iTerm2, executing the command "cat readme.txt" can lead to arbitrary code execution. This vulnerability arises from iTerm2's legitimate features that inadvertently allow such exploits.

blog.calif.io

🔥🔥🔥🔥🔥

5 min

4/17/2026

No more articles to load