Report · doublepulsar.com
Anthropic hacked to deliver remote access trojan
doublepulsar.com
Source published October 30, 2026
Summary: 1 min read
65/100
Summary
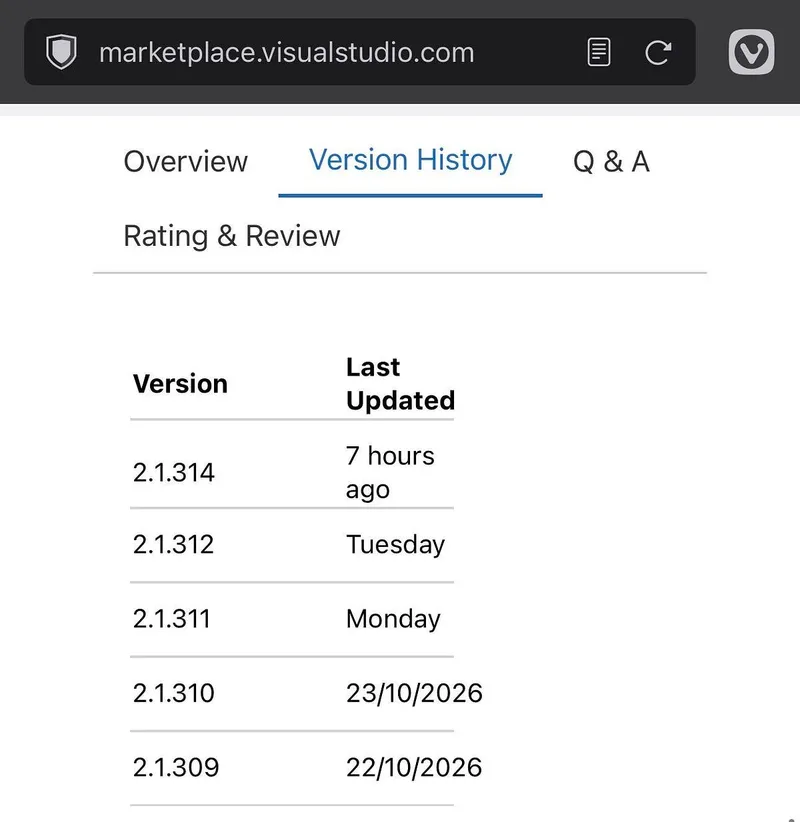
Cursor said a maliciously modified version of Anthropic’s Claude Code extension was published in its VS Code extension marketplace and attempted to install a persistent SSH backdoor on developer computers. Cursor estimated that about 5,000 developer systems were affected. The compromised extension version, 2.1.313, was replaced by version 2.1.314 roughly eight hours later, according to the report; version 2.1.313 is no longer listed on OpenVSX, Visual Studio Marketplace, or Cursor. Cursor said the malicious code collected host and user details including hostname, username, operating system, architecture, home-directory path, environment-variable names, working directories, configured Git email, and public IP address. It attempted to add an attacker-controlled SSH key to authorized_keys, enable local SSH access, and establish a reverse SSH tunnel. Cursor said coding errors meant those steps would generally fail unless Cursor had been launched with administrator privileges. The malware also tried to persist through macOS LaunchAgents or Windows scheduled tasks and sent host details and backdoor status to an HTTP beacon endpoint. The report identified 134.209.82.225 as the reverse-tunnel and command-and-control address and published hashes for affected macOS and Windows VSIX packages.
Key Takeaways
- Cursor said a malicious version of Anthropic’s Claude Code extension, version 2.1.313, was distributed through the Cursor VS Code extension marketplace and was later replaced by version 2.1.314.
- Cursor estimated that approximately 5,000 developer systems were affected by the malicious extension.
- The malicious code attempted to collect system information, install an attacker-controlled SSH key, enable SSH, and create a reverse SSH tunnel.
- Cursor said errors in the malware would generally prevent SSH-backdoor installation unless the application was started with administrator privileges.
- The reported command-and-control infrastructure included HTTP POST requests to 134.209.82.225 on port 8099 and reverse SSH connections to the same IP on port 22.
What the discussion said
The thread spent far more energy correcting the framing than debating Claude itself. Several commenters argued that the incident was a malicious Claude Code extension package distributed through the Open VSX/Cursor ecosystem, not evidence that Anthropic’s core systems or model had been directly compromised. They pointed to the suspect version disappearing from official channels and release records as circumstantial evidence that a publishing credential or release path may have been abused, while others stressed that the available reports did not establish that conclusion. There was broad agreement that an AI coding assistant extension is a potent supply-chain target: it runs in developers’ editors, may have access to repositories and credentials, and in this case reportedly installed a reverse-access mechanism. Readers also pushed back on inflated claims about tens of millions of victims, citing the marketplace operator’s estimate that the affected package reached no more than roughly 5,000 users. The practical takeaway was blunt: install AI developer tooling only from verifiable official sources and treat registry provenance as part of the product’s security boundary. A joking subthread mocked the idea that Claude’s advanced reasoning should somehow have detected or stopped the compromise, rather than offering any serious claim about model-based defense.
Where opinion split
The sharp dispute is whether this should be described as Anthropic being hacked. One side sees the anomalous extension release and its removal from official-looking distribution paths as signs that Anthropic-controlled publishing access was likely compromised. The other says the evidence supports a poisoned third-party marketplace package, and that calling it an Anthropic breach overstates what has been established.
Coverage & discussions
Hacker News · doublepulsar.com
Community discussions
Community Sentiment
Positives
- Marketplace reporting narrowed the blast radius to about 5,000 installs, a meaningful containment signal for teams relying on Claude Code in their development environments.
- Commenters quickly separated sensational claims from the documented package-level incident, helping AI-tool users focus on the actual affected extension and version.
- The discussion treats verified distribution channels as a core safety feature for AI coding assistants, not a cosmetic detail developers can ignore.
Concerns
- A backdoored Claude Code extension can turn an AI assistant embedded in a developer editor into a route for remote machine access, repository exposure, and credential theft.
- Uncertainty over whether a publisher account, registry, or marketplace was breached makes trust in AI developer-tool supply chains harder to assess.
- The incident shows how easily a recognizable AI vendor name can lend credibility to a malicious extension when users cannot verify package provenance.
Related Articles
Backdoor in Claude Code for VS Code extension on the Cursor Marketplace
Oct 30, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026
Anatomy of a Failed (Nation-State?) Attack
Jun 27, 2026
How to compromise your system with a job interview
Aug 20, 2026
The Claude Code Source Leak: fake tools, frustration regexes, undercover mode
Mar 31, 2026