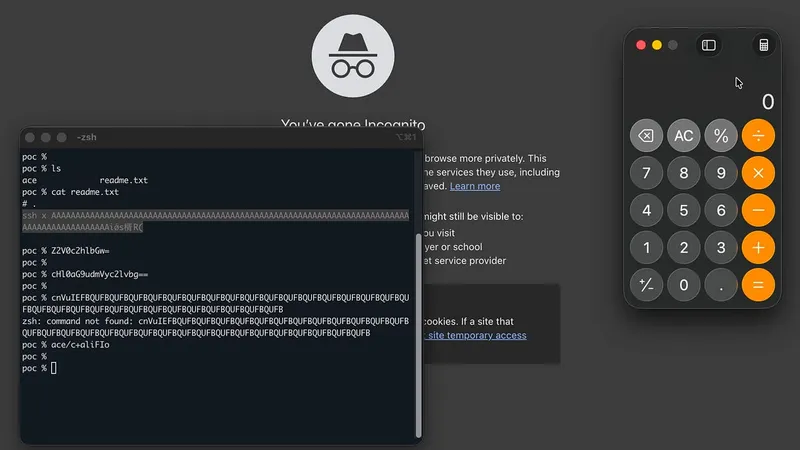
Even "cat readme.txt" is not safe
blog.calif.io
April 17, 2026
5 min read
🔥🔥🔥🔥🔥
62/100
Summary
Using iTerm2, executing the command "cat readme.txt" can lead to arbitrary code execution. This vulnerability arises from iTerm2's legitimate features that inadvertently allow such exploits.
Key Takeaways
- The command "cat readme.txt" in iTerm2 can lead to arbitrary code execution due to a vulnerability in its SSH integration feature.
- iTerm2's SSH integration uses a protocol that allows terminal output to impersonate a trusted conductor, leading to a trust failure.
- The exploit involves a malicious file containing forged terminal escape sequences that trick iTerm2 into executing commands as if they were from a legitimate conductor session.
- The vulnerability highlights the risks associated with terminal emulators and the need for careful handling of terminal output.
Coverage & discussions
Hacker News · blog.calif.io
Community discussions
Community Sentiment
Positives
- The discussion highlights the importance of understanding security vulnerabilities in terminal applications, emphasizing the need for competent engineering to mitigate risks.
- There is a recognition that traditional vulnerability disclosure practices may evolve as AI tools become more prevalent in identifying security flaws.
Concerns
- The recurring nature of vulnerabilities in terminal applications suggests a systemic issue that hasn't been adequately addressed, raising concerns about the reliability of these tools.
- Disclosing vulnerabilities before they are patched could increase the risk of exploitation, indicating a potential oversight in responsible reporting practices.