GitHub bans security researcher who posted zero-day Windows exploits
tomshardware.com
May 28, 2026
6 min read
🔥🔥🔥🔥🔥
69/100
Summary
Microsoft's GitHub has banned security researcher Nightmare-Eclipse after they posted zero-day Windows exploits. The researcher claims this action has ruined their life and has promised further retaliation against the company.
Key Takeaways
- Microsoft banned security researcher Nightmare-Eclipse from GitHub after they posted zero-day Windows exploits, leading the researcher to move to GitLab.
- Eclipse claims that Microsoft ignored their zero-day reports and failed to pay out bug bounties, resulting in financial harm.
- Eclipse has published multiple zero-day exploits for Windows, including vulnerabilities that allow unauthorized access to the SYSTEM user and bypass security features like Defender and BitLocker.
- Experts criticize Microsoft's handling of security reports, suggesting that recent changes in the Microsoft Security Response Center (MSRC) have negatively impacted collaboration with researchers.
Coverage & discussions
Hacker News · tomshardware.com
Community discussions
Community Sentiment
Positives
- The researcher's ability to discover zero-day vulnerabilities highlights the critical role of security researchers in enhancing software safety, even if their methods are controversial.
- Concerns about AI-generated code in Microsoft's software suggest a growing awareness of the need for robust security measures, indicating a shift in how companies approach software development.
Concerns
- Banning a researcher who identifies zero-day vulnerabilities raises ethical questions about how companies handle security research and the potential consequences for the wider security community.
- The perception that Microsoft may be uncomfortable with vulnerabilities existing prior to AI indicates a troubling trend in prioritizing corporate image over genuine security improvements.
Related Articles
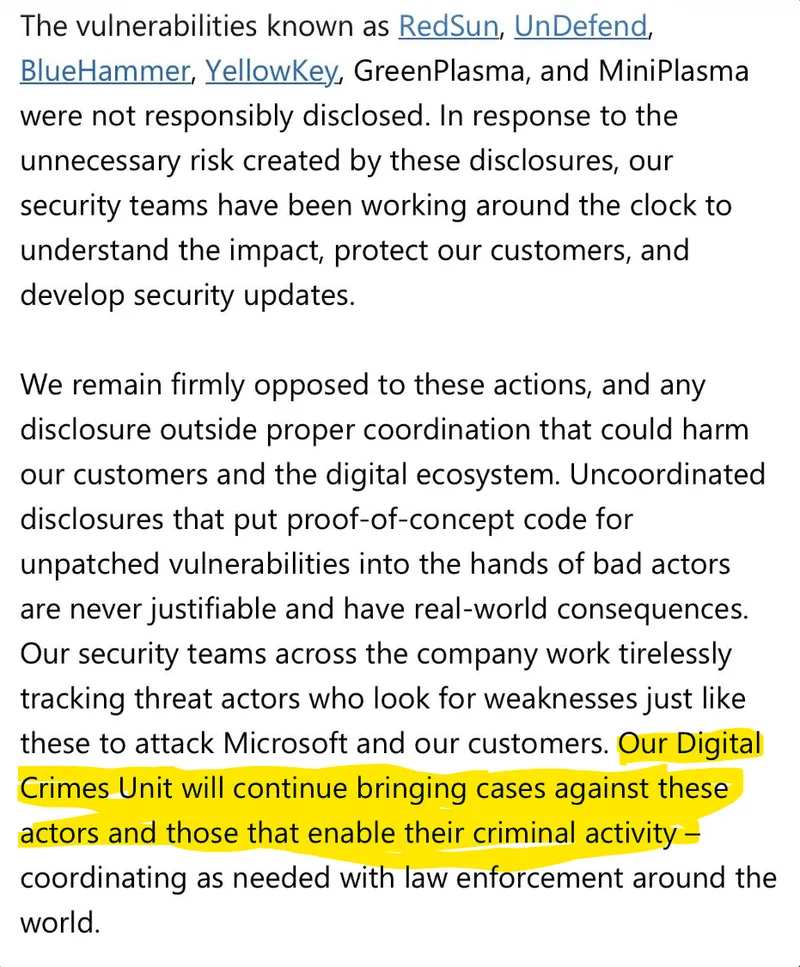
Microsoft's stance on zero day exploits is a dumpster fire of their own making
May 28, 2026
Microsoft Patches a Record 570 Security Flaws
Jul 14, 2026
Decisions that eroded trust in Azure – by a former Azure Core engineer
Apr 2, 2026
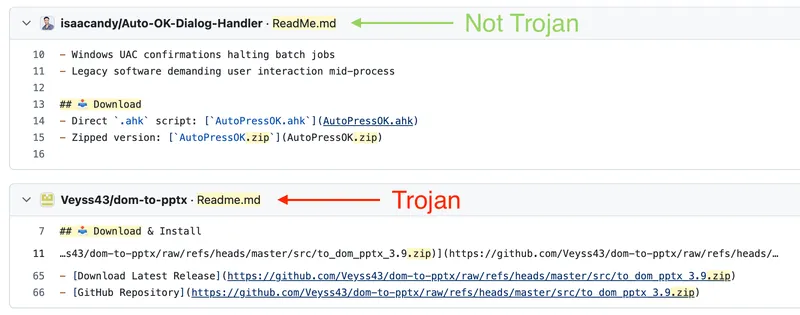
What does GitHub's security team even do?
Jul 26, 2026
I found 10k GitHub repositories distributing Trojan malware
Jun 18, 2026