How kernel anti-cheats work
s4dbrd.github.io
March 15, 2026
45 min read
🔥🔥🔥🔥🔥
64/100
Summary
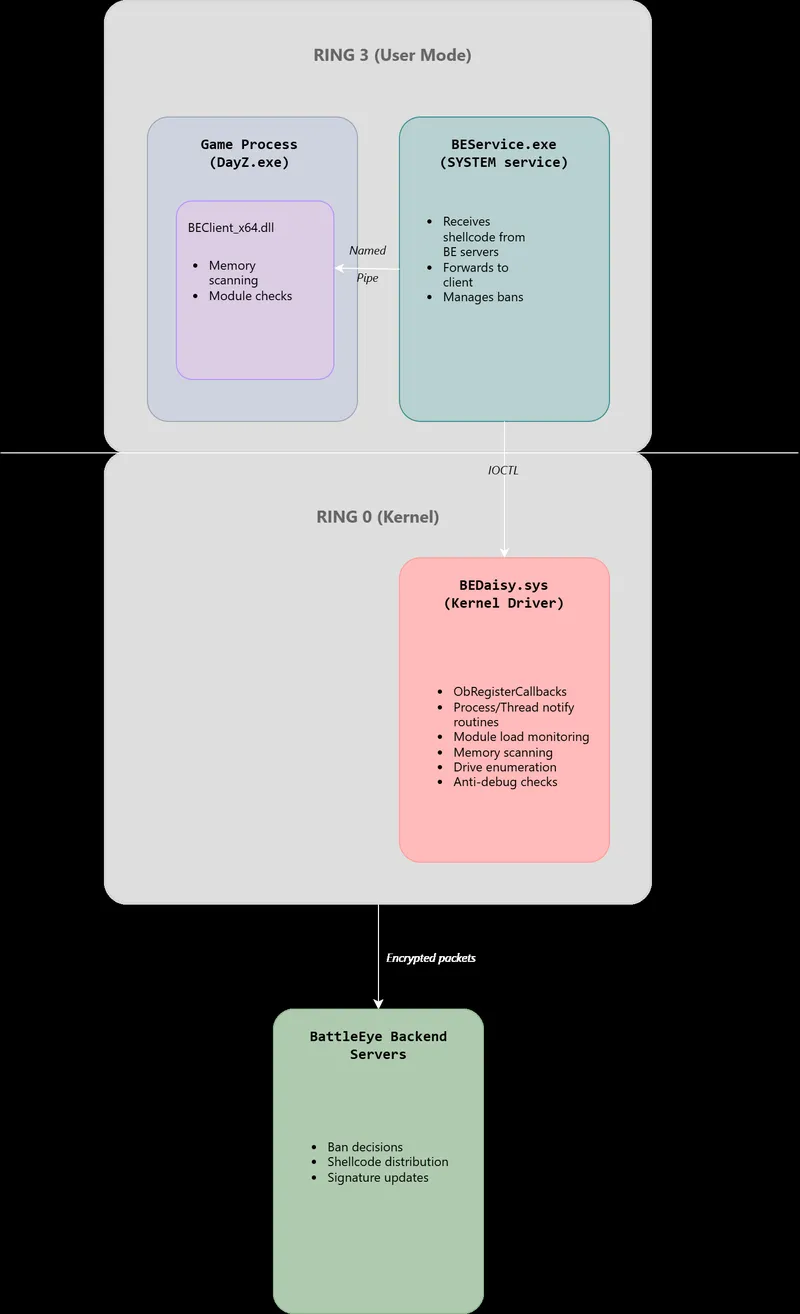
Modern kernel anti-cheat systems operate at the highest privilege level on consumer Windows machines, intercepting kernel callbacks and scanning memory structures. These systems function transparently to detect and prevent cheating in games.
Key Takeaways
- Modern kernel anti-cheat systems operate at the highest privilege level on Windows, allowing them to intercept kernel callbacks and scan memory structures transparently while a game is running.
- Usermode anti-cheat protections are insufficient because they can be bypassed by processes running at higher privilege levels, leading to the development of kernel-mode anti-cheats.
- The ongoing arms race between cheat developers and anti-cheat engineers has escalated from usermode to kernel-mode cheats, and now to hypervisor and PCIe DMA attacks, making cheating increasingly expensive and complex.
- Major anti-cheat systems in competitive gaming include BattlEye, which is used by popular titles such as PUBG and Rainbow Six Siege.
Coverage & discussions
Hacker News · s4dbrd.github.io
Community discussions
Community Sentiment
Positives
- Utilizing machine learning for anomaly detection in gaming could effectively identify cheaters, providing a sophisticated solution to a complex problem.
- The idea of a matchmaking pool with optional anticheat could foster a unique gaming environment, allowing players to choose their level of security.
Concerns
- Modern cheats exploit hypervisors and BIOS patching, undermining the integrity of anticheat systems and posing significant security risks.
- Kernel-level anticheat mechanisms can compromise system stability, leading to potential security vulnerabilities and crashes.