I found 10k GitHub repositories distributing Trojan malware
orchidfiles.com
June 18, 2026
8 min read
🔥🔥🔥🔥🔥
75/100
Summary
A large-scale malware distribution campaign on GitHub has been identified, involving 10,000 repositories that distribute Trojan malware. These repositories originate from different contributors and share a common pattern, enabling the creation of a script to find them.
Key Takeaways
- A large-scale malware distribution campaign was identified on GitHub, involving 10,000 repositories that distribute Trojan malware.
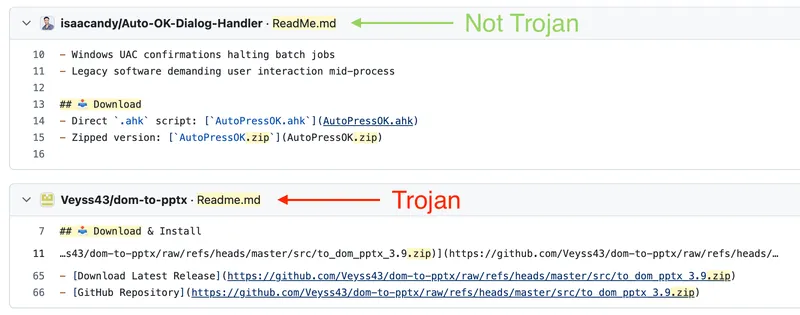
- The repositories share a common pattern of frequently deleting and re-pushing commits that only update the readme file with a link to a zip archive.
- The zip files contain executable files that are detected as Trojans when submitted directly, despite showing no viruses when the links are scanned on VirusTotal.
- A script was developed to analyze GitHub repositories based on specific patterns, focusing on those that are updated every few hours.
Coverage & discussions
Hacker News · orchidfiles.com
Community discussions
Community Sentiment
Positives
- The ability to audit open-source software provides a level of transparency that proprietary software lacks, allowing users to verify the code they run.
- Using password managers can enhance security by preventing users from entering credentials on phishing sites, highlighting the importance of good security practices.
Concerns
- The prevalence of Trojan malware in GitHub repositories raises serious concerns about the reliability of open-source software as a safe option for developers.
- GitHub's lack of effective moderation for malicious repositories undermines trust in the platform, making it a risky environment for users seeking legitimate software.
Related Articles
What does GitHub's security team even do?
Jul 26, 2026
Glassworm Is Back: A New Wave of Invisible Unicode Attacks Hits Repositories
Mar 15, 2026
Keyv and friends compromised in active Shai-Hulud supply chain attack
Aug 4, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026
Anatomy of a Failed (Nation-State?) Attack
Jun 27, 2026