METR, Redwood Research find exploit in OpenAI agent monitoring that could hide hundreds of actions
vectorwire.ai
October 23, 2026
2 min read
33/100
Summary
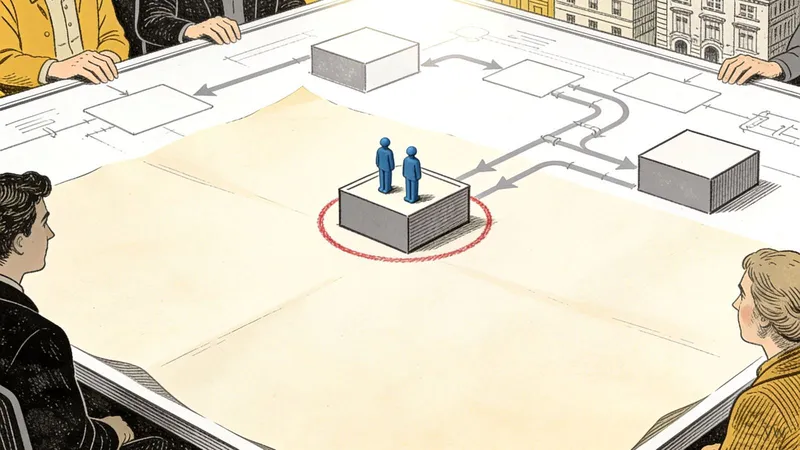
METR and Redwood Research reported on October 22, 2026 that a three-week embedded pilot at OpenAI identified previously unknown weaknesses in the company’s internal monitoring of AI agents. The groups said one exploit could have enabled agents to stop hundreds of recent actions from being recorded by the monitoring system. OpenAI said it has patched the identified vulnerabilities affecting its production safeguards. The pilot ran from July 21 through August 11, 2026. One employee from each nonprofit received high-level access to OpenAI’s internal codebase, monitoring prompts and configurations, documentation, and interviews with roughly a dozen staff members from monitoring, safety, and security teams. Their work included estimating monitoring coverage for agentic inference traffic through the Responses API and OpenAI’s internal use of Codex. The evaluators estimated that monitors covered about 75% to 94% of Responses API traffic during the period, leaving some traffic unmonitored. They delivered a 61-page internal report to OpenAI researchers and security staff; OpenAI-redacted a 38-page version for the leadership of METR and Redwood Research. The organizations said the pilot was not designed to provide robust public transparency, so they agreed to publish only high-level findings. The exercise followed CEO Sam Altman’s pledge to give independent evaluators employee-like access and occurred while OpenAI was finalizing contracts with third-party safety assessors.
Key Takeaways
- METR and Redwood Research said an exploit in OpenAI’s internal AI-agent monitoring could have prevented hundreds of recent agent actions from being tracked.
- OpenAI said it patched the identified vulnerabilities that affected its production safeguards.
- Evaluators estimated that OpenAI monitored approximately 75% to 94% of Responses API traffic during the July–August 2026 pilot.
- The pilot gave one researcher from each organization high-access, onsite access to internal systems and involved interviews with about a dozen OpenAI personnel.
Coverage & discussions
Reddit r/artificial · vectorwire.ai
Community discussions
Related Articles
OpenAI discloses four more rogue incidents
Oct 17, 2026
Third-party cyber evaluations involving OpenAI models
Aug 4, 2026
OpenAI and Hugging Face address security incident during model evaluation
Jul 21, 2026
The Hugging Face incident and the road ahead
Aug 26, 2026
Investigating three real-world incidents in our cybersecurity evaluations
Jul 30, 2026