Plex vulnerabilities being exploited in the wild to drop a cryptominer
boredhackerblog.info
October 19, 2026
3 min read
54/100
Summary
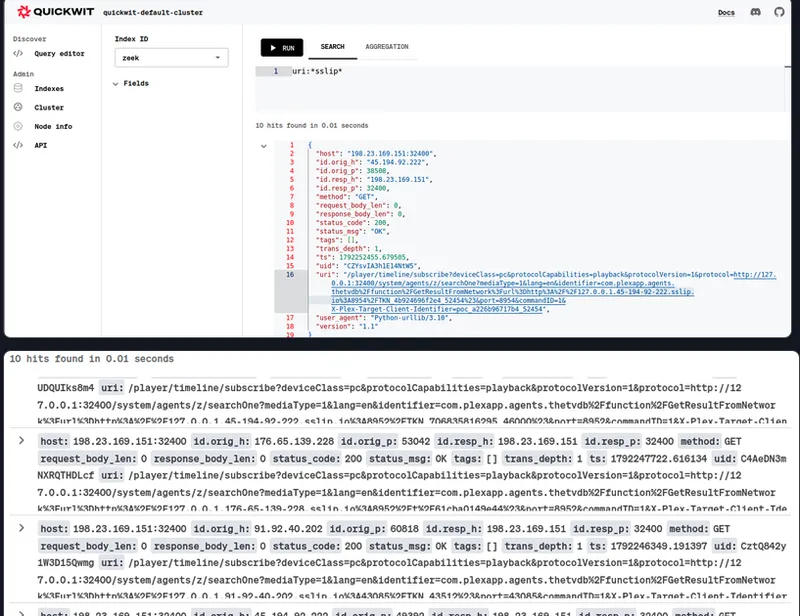
Attackers began exploiting unpatched Plex Media Server instances in October 2026 after Plex disclosed important security updates on September 1 for version 1.43.2 and earlier. Four vulnerabilities—CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656—can be chained to achieve remote code execution, according to the researcher behind the Plex2Shell proof of concept released October 16. A vulnerable Plex honeypot recorded exploitation attempts from 45.194.92.222, 91.92.40.202, and 176.65.139.228 on October 17. After outbound network access was enabled, the honeypot logged a file download from 217.60.194.116. Observed payloads included a Docker file and an UPX-packed executable identified as a cryptominer. Subsequent activity also deployed XMRig and a program named myawesomeproxy. The proxy program states that running it permits external use of the device’s internet traffic, and observed network traffic was associated with proxystream.st. Detection packet captures and artifacts are available through the Plex2Shell and BoredHackerBlog GitHub repositories. Plex server operators running affected older versions should apply Plex’s security updates and investigate the listed indicators of compromise.
Key Takeaways
- Plex disclosed security updates on September 1, 2026, for Plex Media Server version 1.43.2 and earlier; four CVEs were later linked to a remote-code-execution chain.
- A honeypot recorded exploitation attempts from 45.194.92.222, 91.92.40.202, and 176.65.139.228, with payload downloads observed from 217.60.194.116.
- Observed payloads included a cryptominer, XMRig, and myawesomeproxy, which states that it may use a victim device’s internet traffic externally.
- The Plex2Shell proof of concept and associated detection resources provide code and packet captures for identifying exploitation activity.
What the discussion said
The thread was overwhelmingly about Plex security, exposed home-media servers, overdue updates, and a deteriorating client experience rather than AI. The one AI-relevant point was a report that the Plex2Shell proof of concept used an LLM to combine multiple known vulnerabilities into a working attack chain. That detail sharpened concern because the individual failures described were not exotic research-grade flaws: commenters saw basic authorization validation and URL-checking mistakes that became far more dangerous once assembled into an automated exploitation path. There was no real debate over whether the model itself had demonstrated sophisticated offensive reasoning. Readers instead treated it as an unsettling example of how generative tools can lower the effort required to turn public CVEs into usable malware delivery. The actual payloads, especially cryptominers and possible DDoS participation, were viewed as mundane but still damaging evidence that attackers exploit neglected infrastructure quickly. The broader arguments about whether Plex should be internet-facing, whether updates should be automatic, and whether its interface has worsened do not materially assess AI and therefore offer little basis for an AI-specific verdict. The limited AI discussion thus lands negative: LLM assistance appears to have made exploit composition more accessible, while the thread offered no countervailing evidence of defensive AI use or meaningful safeguards.
Coverage & discussions
Hacker News · boredhackerblog.info
Community discussions
Community Sentiment
Concerns
- An LLM reportedly stitched several existing Plex weaknesses into a usable exploit chain, illustrating how generative tools can turn scattered CVEs into practical attacks with much less specialist effort.
- The attack path reportedly hinged on elementary security validation failures, making AI-assisted exploit assembly especially alarming because the barrier was integration rather than breakthrough research.
Related Articles
Anonymous GitHub account mass-dropping undisclosed 0-days
Jun 27, 2026
I found 10k GitHub repositories distributing Trojan malware
Jun 18, 2026
Malware developers added nuclear and biological weapons text to to their spyware
Jun 11, 2026
A hacker broke into John Deere and SharkNinja with an army of AI agents
Oct 19, 2026
Big Fish: Exploiting a 37-Year-Old Kernel Bug in OpenBSD
Oct 16, 2026