Rsync and outrage
medium.com
June 3, 2026
7 min read
🔥🔥🔥🔥🔥
56/100
Summary
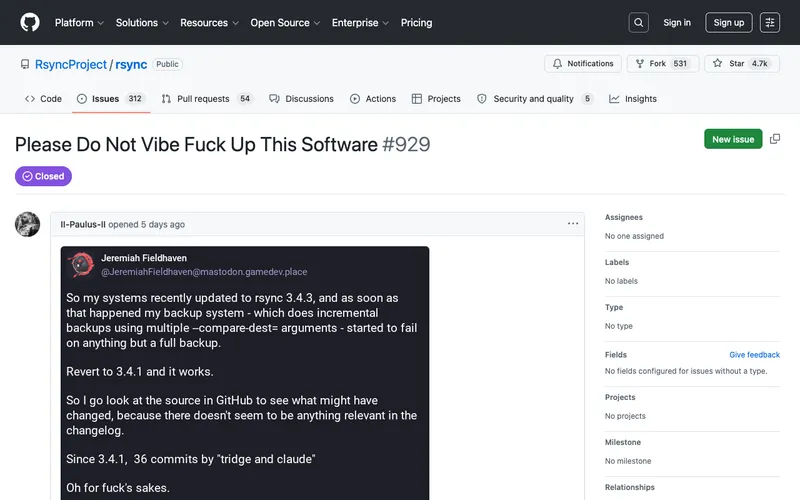
Rsync maintainer has received an influx of security reports, many of which are generated by AI. This situation has led to significant frustration among developers of open source packages.
Key Takeaways
- The maintainer of rsync has experienced a surge in security reports, many of which are generated by AI.
- The rsync test suite was rewritten in Python, utilizing AI tools for grunt work while ensuring thorough design and validation by the maintainer.
- The landscape of software engineering and IT security has dramatically changed, necessitating new approaches to handling security issues.
- The 3.4.3 release of rsync had regressions in some use cases due to prioritizing security fixes, and the maintainer is actively addressing these issues.
Coverage & discussions
Hacker News · medium.com
Community discussions
Community Sentiment
Positives
- The project gained significant attention due to the coding approach, potentially leading to valuable community support for future improvements.
- The discussion around the bugs highlights the importance of rigorous testing and version management in software development, which is crucial for maintaining reliability.
Concerns
- Basic bugs introduced in the latest update, such as issues with absolute paths and links mode, raise concerns about the quality control processes in place.
- The outrage over the minor version release reflects a broader skepticism about the use of AI in software development, particularly when it leads to regressions in core functionality.
- The perception that AI contributions can lower standards in software quality is troubling, indicating a potential backlash against AI-assisted development.