SQLite Critical CVEs or LLM Slop?
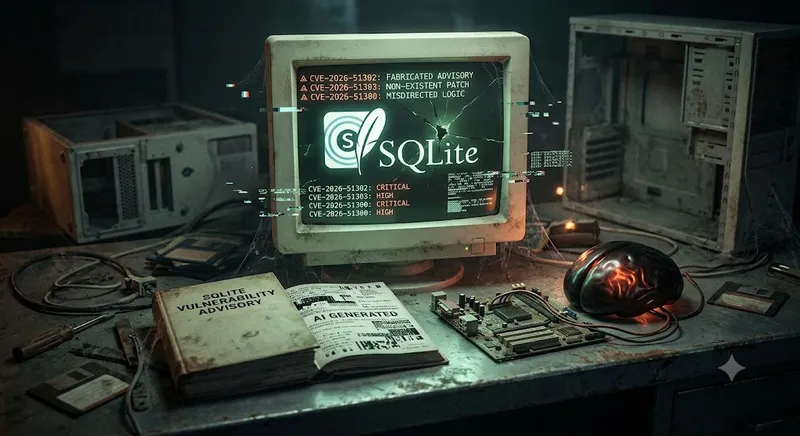
research.jfrog.com
August 3, 2026
7 min read
🔥🔥🔥🔥🔥
71/100
Summary
A GitHub repository published multiple SQLite vulnerability advisories, which were flagged as critical by NVD and CISA. JFrog security researchers found that the cited code did not exist in the referenced versions, and the proof-of-concept payloads failed to trigger the vulnerabilities.
Key Takeaways
- A GitHub repository published multiple SQLite vulnerability advisories that were later found to be largely fabricated or inaccurate, with claims of critical vulnerabilities that did not exist in the referenced code.
- JFrog security researchers verified the advisories and determined that none were listed on SQLite’s official advisory page, indicating they may be AI-generated content.
- The severity score for CVE-2026-51302 was downgraded from 10.0 (Critical) to 7.6 (High) after further investigation revealed inconsistencies in the advisory.
- Testing of the reported vulnerabilities showed that proof-of-concept payloads did not trigger any crashes, confirming the absence of the claimed vulnerabilities.
Coverage & discussions
Hacker News · research.jfrog.com
Community discussions
Community Sentiment
Positives
- LLMs are discovering legitimate CVEs, which shows their potential utility in security contexts despite the noise.
- Some commenters believe that understanding the limitations of LLMs can enhance their effectiveness, leading to better user outputs.
Concerns
- The overhyped capabilities of LLMs are leading to significant credibility issues, especially when they misidentify vulnerabilities.
- Many commenters are concerned that LLMs are generating a flood of unverified CVEs, complicating the process of identifying genuine threats.
- There's a strong sentiment that LLMs are being misused by inexperienced individuals, inflating their perceived value in the tech industry.
Related Articles
Anonymous GitHub account mass-dropping undisclosed 0-days
Jun 27, 2026
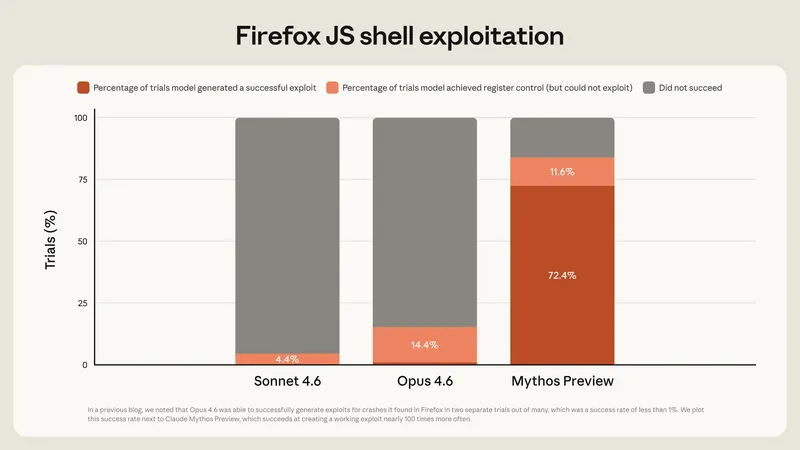
Assessing Claude Mythos Preview's cybersecurity capabilities
Apr 7, 2026
The obscure trust looming over Anthropic's IPO
Oct 19, 2026

macOS 15.8.2 Breaks OpenGL
Oct 18, 2026
Omarchy development practices lead to predictable security issues
Aug 26, 2026