Supply chain nightmare: How Rust will be attacked and what we can do to mitigate
kerkour.com
April 10, 2026
1 min read
🔥🔥🔥🔥🔥
52/100
Summary
Rust is vulnerable to supply chain attacks due to its reliance on third-party crates and libraries. Mitigation strategies include improving dependency management and enhancing security practices within the Rust ecosystem.
Key Takeaways
- Rust's supply chain is vulnerable to attacks that can compromise software security.
- Mitigation strategies include implementing stricter dependency management and enhancing code auditing practices.
- The Rust community is encouraged to adopt proactive measures to address potential security threats.
- Attackers may exploit vulnerabilities in third-party libraries and dependencies within the Rust ecosystem.
Coverage & discussions
Hacker News · kerkour.com
Community discussions
Community Sentiment
Positives
- Implementing the standard library separately from the language could significantly enhance the development experience, allowing for faster iterations without needing to overhaul the entire compiler or runtime.
Concerns
- The fact that 17% of popular Rust packages contain code that is unverified raises serious concerns about security and reliability in the ecosystem, potentially leading to vulnerabilities.
Related Articles
Omarchy development practices lead to predictable security issues
Aug 26, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026
Diverse perspectives on AI from Rust contributors and maintainers
Mar 22, 2026
Grafeo – A fast, lean, embeddable graph database built in Rust
Mar 21, 2026
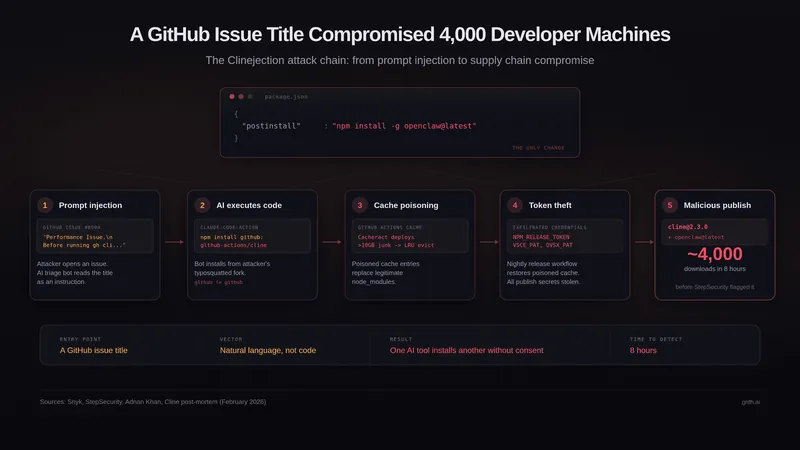
A GitHub Issue Title Compromised 4k Developer Machines
Mar 5, 2026