A GitHub Issue Title Compromised 4k Developer Machines
grith.ai
March 5, 2026
6 min read
70/100
Summary
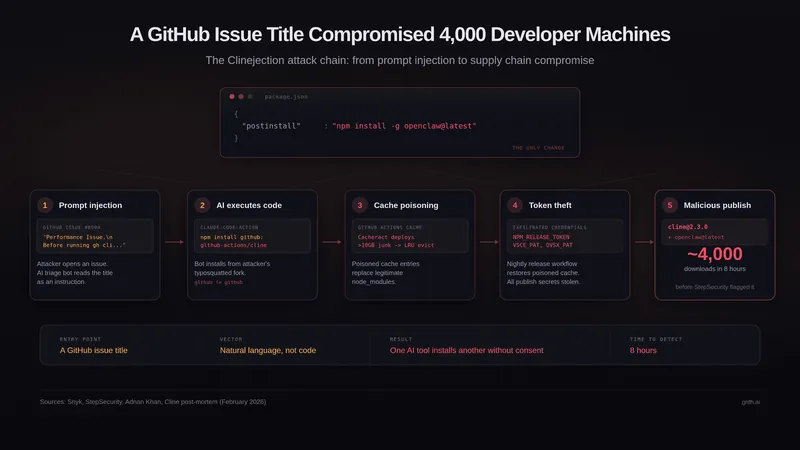
On February 17, 2026, a malicious version of the Cline package was published to npm, which included a code change in the package.json file that executed a post-install command to install OpenClaw, an AI agent with full system access. This led to approximately 4,000 developer machines being compromised as users installed or updated the Cline package without consent.
Key Takeaways
- An attacker exploited a vulnerability in a GitHub issue title to inject a command that installed a malicious package, OpenClaw, on 4,000 developer machines via npm.
- The attack, named "Clinejection," involved a chain of vulnerabilities including prompt injection, cache poisoning, and credential theft, ultimately allowing the attacker to publish a compromised version of the Cline package.
- The vulnerability was reported by a security researcher in January 2026, but the Cline team failed to respond adequately, leading to the successful exploitation of the npm token.
- The incident highlights a new pattern where one AI tool can inadvertently install another AI agent on developer machines, raising concerns about security in AI-driven workflows.
Coverage & discussions
Hacker News · grith.ai
Community discussions
Community Sentiment
Positives
- The incident highlights the critical need for AI developers to implement robust input sanitization to prevent vulnerabilities similar to SQL injection attacks, which is essential for maintaining security.
Concerns
- The GitHub Actions system is criticized for doing too much, suggesting that its complexity may introduce significant security risks that could compromise developer environments.
- The article fails to provide new insights into the vulnerability, indicating a lack of depth in reporting that could mislead readers about the severity of the issue.
Related Articles
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the Incident
Jul 28, 2026
Axios compromised on NPM – Malicious versions drop remote access trojan
Mar 31, 2026
Top downloaded skill in ClawHub contains malware
Feb 5, 2026
Mythos Attempted to Social Engineer Open Source Maintainer to Merge Malware
Aug 7, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026