Anonymous GitHub account mass-dropping undisclosed 0-days
github.com
June 27, 2026
4 min read
🔥🔥🔥🔥🔥
74/100
Summary
The GitHub repository "exploitarium" contains a collection of public exploit proof-of-concepts (PoCs) and vulnerability research writeups, with a focus on serious vulnerabilities. AI was utilized to automate the fuzzing workflow using GPT-5.5-3-Codex-Spark, allowing for efficient testing with minimal manual intervention.
Key Takeaways
- The GitHub repository "exploitarium" contains a collection of public proof-of-concept (PoC) exploits and vulnerability research writeups, with a focus on serious vulnerabilities.
- AI was utilized to automate the fuzzing workflow, specifically using GPT-5.5-3-Codex-Spark, although the author emphasizes that human oversight and a good harness are crucial for effective vulnerability identification.
- The repository includes various PoCs for different software vulnerabilities, with new entries being added regularly as self-contained folders.
- The author has a background in the field, having published multiple papers on fuzzing methodology, and aims to motivate others to engage in vulnerability research.
Coverage & discussions
Hacker News · github.com
Community discussions
Community Sentiment
Positives
- The increasing sophistication of AI tools is expected to lead to more complex vulnerabilities, indicating a transition in how security issues are identified and reported.
- AI's ability to curate datasets and improve prompt handling could enhance the overall quality of vulnerability reporting, making it more reliable.
Concerns
- Many of the so-called '0-day' vulnerabilities may actually stem from previously disclosed CVEs, diluting the term's significance and causing confusion in the community.
- AI tools are generating a high volume of alerts, often labeling trivial issues as significant vulnerabilities, which can overwhelm developers and obscure real threats.
- The perception that AI is 'getting smart' in vulnerability detection is misleading; it's more about improved data handling rather than true intelligence.
Related Articles
Copy Fail – CVE-2026-31431
Apr 29, 2026
Keyv and friends compromised in active Shai-Hulud supply chain attack
Aug 4, 2026
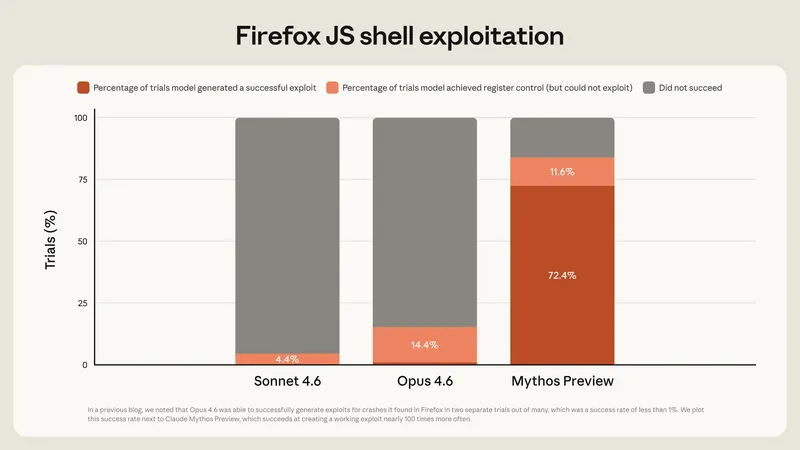
Assessing Claude Mythos Preview's cybersecurity capabilities
Apr 7, 2026
SQLite Critical CVEs or LLM Slop?
Aug 3, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026