Codex Hacked a Samsung TV
blog.calif.io
April 16, 2026
11 min read
🔥🔥🔥🔥🔥
60/100
Summary
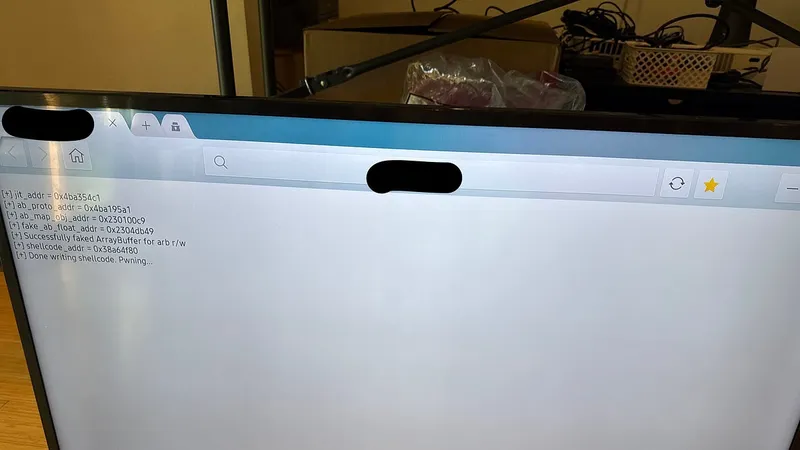
Codex gained access to a Samsung TV by exploiting a vulnerability in its browser application, resulting in a root shell being opened. The research demonstrates the capability of AI to hack hardware devices, with no significant damage caused to the TV during the process.
Key Takeaways
- Codex successfully gained root access on a Samsung TV by exploiting a browser application vulnerability.
- The research involved providing Codex with a controlled environment to enumerate the target and adapt its tooling to Samsung's execution restrictions.
- The process required Codex to audit the firmware source, validate memory primitives, and execute commands through a shell session on the TV.
- The goal was to identify and exploit a vulnerability for privilege escalation without providing specific exploits or bugs to Codex.
Coverage & discussions
Hacker News · blog.calif.io
Community discussions
Community Sentiment
Positives
- Codex enabled a user to create a reliable Python API for their router, showcasing its practical application in overcoming complex authentication challenges.
- The ability to analyze firmware source code with Codex highlights its potential for identifying vulnerabilities, which is crucial for enhancing device security.
- Users are successfully leveraging AI models like Codex and Claude to automate tasks and discover undocumented features, demonstrating their utility in real-world scenarios.
Concerns
- Concerns were raised about the ease with which AI models could exploit vulnerabilities, suggesting a potential risk in AI's capabilities for hacking.
- The discussion around Samsung TVs indicates a long-standing issue with device security, implying that even advanced models may not significantly improve safety.
Related Articles
Assessing Claude Mythos Preview's cybersecurity capabilities
Apr 7, 2026
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the Incident
Jul 28, 2026
Even "cat readme.txt" is not safe
Apr 17, 2026
C2PA Cameras Do Not Survive Contact with Reality
Aug 25, 2026
VMs won't contain cyber-capable agents
Aug 26, 2026