GitLost: We Tricked GitHub's AI Agent into Leaking Private Repos
noma.security
July 8, 2026
5 min read
68/100
Summary
Noma Labs identified a prompt injection vulnerability in GitHub's Agentic Workflows, allowing unauthenticated attackers to access private repository data by posting a crafted GitHub Issue in a public repository within the same organization. This vulnerability has been named GitLost.
Key Takeaways
- Noma Labs identified a prompt injection vulnerability in GitHub’s Agentic Workflows, named GitLost, allowing unauthorized access to private repositories through crafted GitHub Issues in public repositories.
- The vulnerability enables attackers to execute commands by submitting benign-looking issues, which the GitHub agent processes without verifying the trustworthiness of the content.
- Exploiting the GitLost vulnerability requires no coding skills or credentials; an attacker only needs to create an issue in a public repository associated with the target organization.
- The GitHub agent, when triggered by specific workflow actions, can inadvertently expose private repository data by posting it publicly as a comment.
Coverage & discussions
Hacker News · noma.security
Community discussions
Community Sentiment
Positives
- Some commenters see prompt injection as a critical issue that demands robust defenses, paralleling SQL injection vulnerabilities — a call to arms for better AI safety.
- There's a recognition that organizations need to properly scope LLM access to prevent leaks, hinting at a path forward for responsible AI deployment.
Concerns
- Many users are frustrated with large corporations like Microsoft pushing half-baked AI solutions, fearing a breaking point for consumer trust.
- There's skepticism about GitHub's handling of AI features, with users questioning the responsibility and security of private repositories in the face of these vulnerabilities.
- The consensus is that misconfiguration and poor scoping of agent permissions led to this vulnerability, highlighting a systemic failure in AI design and governance.
Related Articles
Mythos Attempted to Social Engineer Open Source Maintainer to Merge Malware
Aug 7, 2026
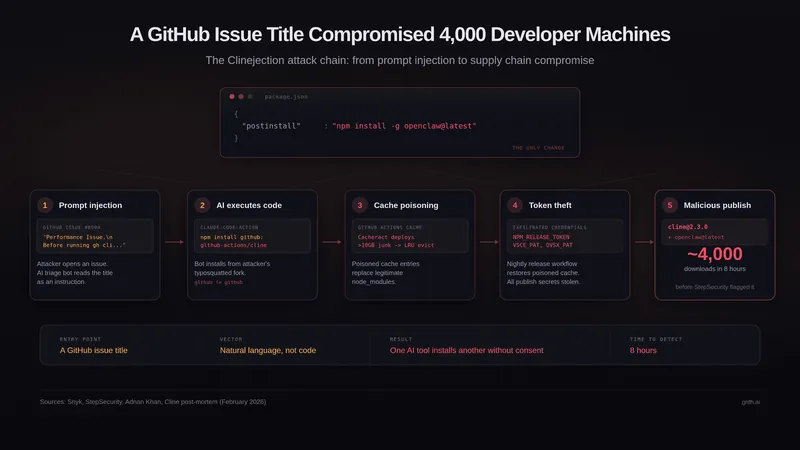
A GitHub Issue Title Compromised 4k Developer Machines
Mar 5, 2026
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown
Apr 28, 2026
AI-Generated GitHub Copilot “Autofix” Allowed Compromise of Snowflake's Jira
Aug 17, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026