Incident CVE-2026-LGTM
nesbitt.io
June 26, 2026
10 min read
69/100
Summary
A security incident was reported involving a malicious package that affected all systems, including some not owned by the organization. The incident was resolved after 96 hours and involved a total of 2.1 trillion billable tokens, with the AI-augmented defense strategy functioning as intended.
Key Takeaways
- A security incident involving a malicious package was resolved after an attacker’s autonomous agent accessed a restricted file, triggering credential exfiltration across affected systems.
- The malicious package passed through seven independent AI-powered security gates, each failing to identify the threat for different reasons.
- The incident duration was 96 hours, with a total of 2.1 trillion tokens billed for the response.
- The AI-augmented defense strategy, implemented in response to a previous vulnerability (CVE-2024-YIKES), did not prevent the breach.
Coverage & discussions
Hacker News · nesbitt.io
Community discussions
Community Sentiment
Positives
- The satire effectively highlights the absurdities of current AI practices, making it relatable and thought-provoking for tech professionals.
- The comedic elements in the report serve as a mirror to real-world scenarios, emphasizing the potential pitfalls of relying too heavily on AI in software development.
Concerns
- The overwhelming complexity of AI-driven processes can lead to cognitive overload, suggesting a troubling future where human oversight is diminished.
- The portrayal of AI systems as potentially flawed and prone to errors raises concerns about their reliability in critical software development tasks.
Related Articles
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the Incident
Jul 28, 2026
We May Be Living Through the Most Consequential Hundred Days in Cyber History
Apr 13, 2026
The Hugging Face incident and the road ahead
Aug 26, 2026
AI Meets Cryptography 1: What AI Found in Cloudflare's Circl
Jul 7, 2026
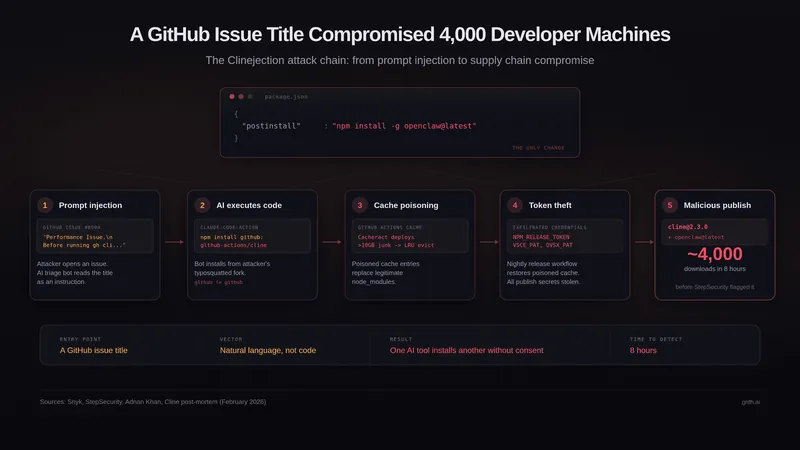
A GitHub Issue Title Compromised 4k Developer Machines
Mar 5, 2026