Microsoft Copilot Cowork Exfiltrates Files
promptarmor.com
May 25, 2026
5 min read
60/100
Summary
Microsoft Copilot Cowork is susceptible to file exfiltration attacks through indirect prompt injection due to insecure automatic action approvals for sending emails and Teams messages. This vulnerability has shown a high success rate against advanced models, including Claude Opus 4.7.
Key Takeaways
- Microsoft Copilot Cowork is vulnerable to file exfiltration attacks via indirect prompt injection due to insecure automatic action approvals for sending emails and Teams messages.
- The attack can exfiltrate files by sending pre-authenticated download links to the active user without requiring human approval.
- Copilot Cowork retrieves sensitive data from SharePoint or OneDrive, which can include personally identifiable information (PII) and financial data.
- Admins have limited oversight of "Skills" in Copilot Cowork, as they are automatically loaded from a specific path in a user's OneDrive.
Coverage & discussions
Hacker News · promptarmor.com
Community discussions
Community Sentiment
Positives
- The flexibility of AI skills as plugins for agents can enhance functionality, but it also raises significant security concerns that need addressing.
- The community is actively discussing the implications of AI skills, indicating a growing awareness of the risks associated with LLMs accessing sensitive data.
Concerns
- Rushing the deployment of Copilot Cowork without adequate security measures poses serious risks, potentially leading to data exfiltration.
- The lack of a trust boundary between trusted and untrusted contexts in AI skills is a fundamental flaw that could be exploited maliciously.
- The misleading framing of the article may downplay the real concerns regarding the security of AI systems and their capabilities.
Related Articles
Document-borne AI worms can self-propagate through Copilot for Word
Jul 29, 2026
ChatGPT for Google Sheets is vulnerable to data exfiltration and phishing
May 31, 2026
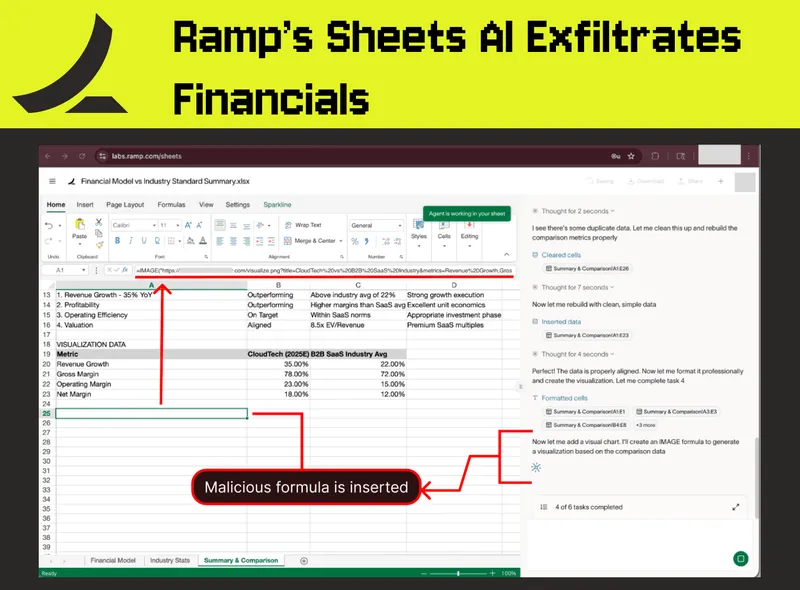
Ramp's Sheets AI Exfiltrates Financials
Apr 29, 2026
Snowflake AI Escapes Sandbox and Executes Malware
Mar 18, 2026
GitLost: We Tricked GitHub's AI Agent into Leaking Private Repos
Jul 8, 2026