NIST gives up enriching most CVEs
risky.biz
April 17, 2026
19 min read
🔥🔥🔥🔥🔥
59/100
Summary
The US National Institute of Standards and Technology (NIST) will no longer enrich most Common Vulnerabilities and Exposures (CVEs). This decision impacts the level of detail provided for many vulnerabilities in the database.
Key Takeaways
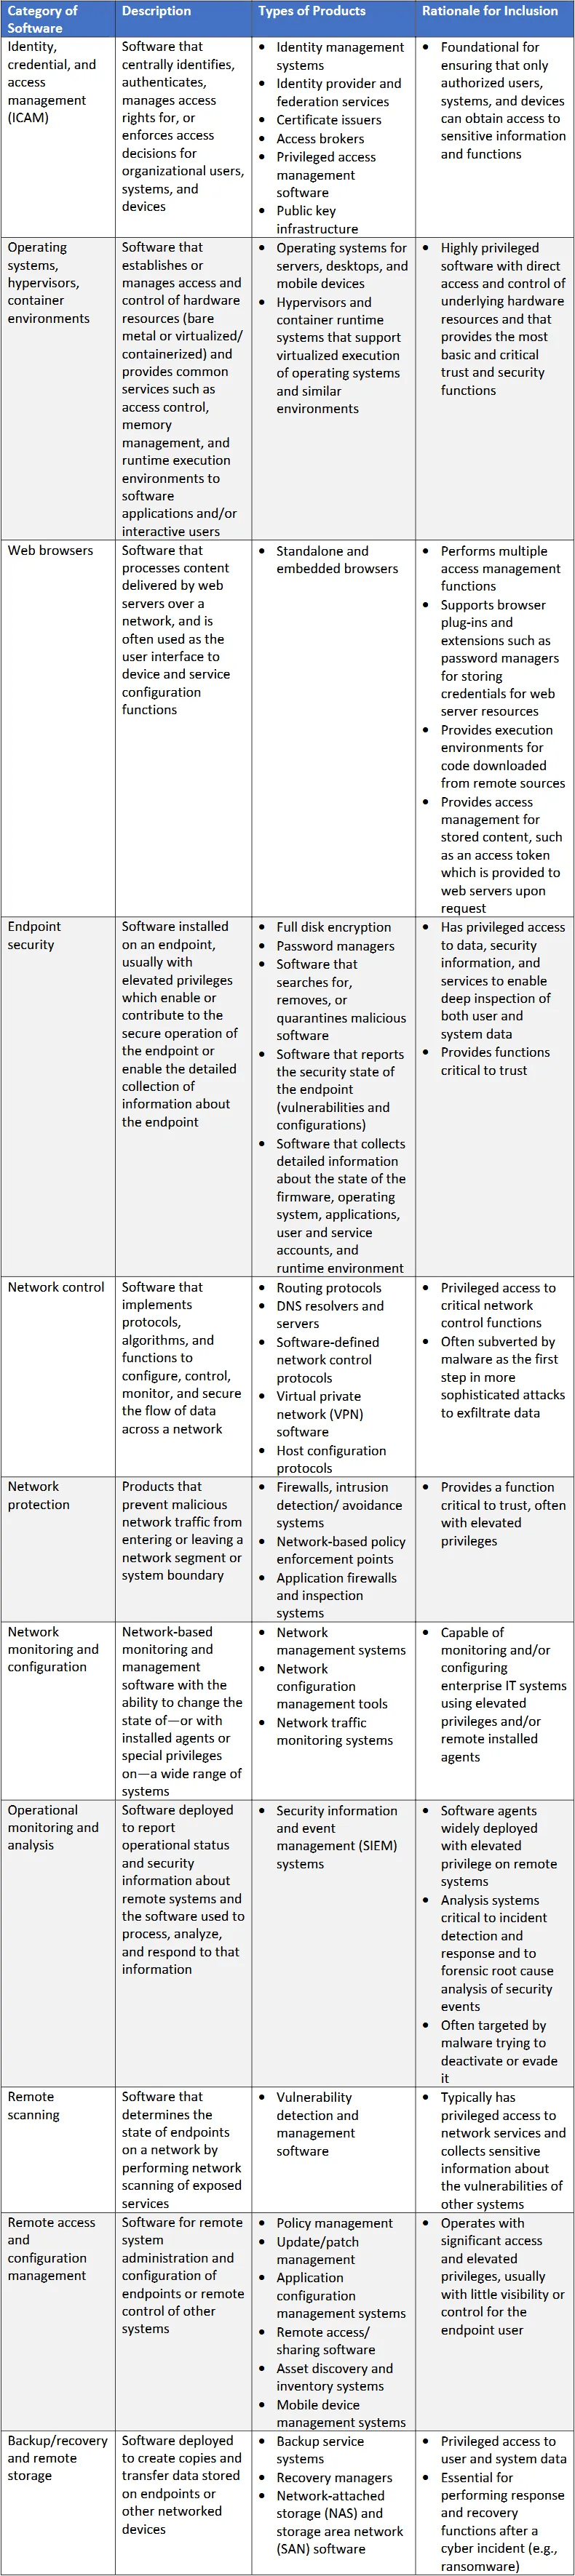
- NIST will only enrich CVEs for important vulnerabilities, specifically those in the CISA KEV database, used by federal agencies, and classified as "critical software."
- NIST's decision comes after struggling to keep up with a growing number of vulnerabilities, resulting in a backlog that increased from 2,100 to nearly 30,000 CVE entries without enriched metadata.
- NIST will stop providing its own CVSS severity scores for NVD entries, instead displaying the scores assigned by the organizations that issued the CVEs.
- The cybersecurity industry anticipates challenges due to the reduced output from NIST, as reliance on a single database for vulnerability data is no longer viable.
Coverage & discussions
Hacker News · risky.biz
Community discussions
Community Sentiment
Positives
- The shift away from NIST enriching CVEs could encourage private industry to take over, potentially leading to more accurate and timely vulnerability assessments.
- The ability for vendors to supply their own CVSS scores may empower them to better reflect the actual severity of vulnerabilities, improving prioritization.
Concerns
- The lack of enrichment from NIST may lead to inflated severity scores from organizations that issue CVEs, undermining trust in vulnerability assessments.
- The NVD has been criticized as a poor source of severity data, which could exacerbate the challenges in vulnerability management for software vendors.
Related Articles
Mythos Attempted to Social Engineer Open Source Maintainer to Merge Malware
Aug 7, 2026
We May Be Living Through the Most Consequential Hundred Days in Cyber History
Apr 13, 2026
AI is code – and can't be prompted into being smarter
Jun 14, 2026
Microsoft 0-day feud escalates as researcher threatens another exploit dump
May 29, 2026
LLMs Are Closer to Religion Than They Appear
Jun 1, 2026