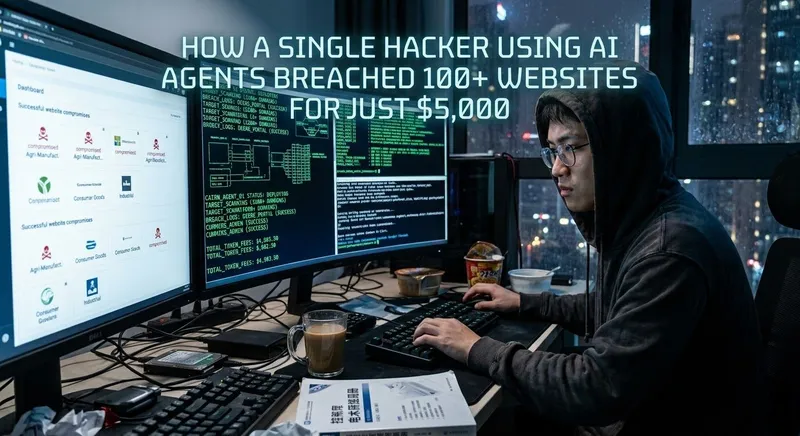
One Hacker Used AI Agents to Breach 100+ Company Websites for About $5,000
kylesinvestigation.com
October 20, 2026
3 min read
21/100
Summary
NorForge, a threat-intelligence firm, said a Chinese-speaking operator used autonomous AI agents through the open-source Cairn platform to target more than 1,200 websites beginning September 25, 2026. The agents reportedly compromised sites associated with more than 100 companies, primarily in the United States, Canada, Australia and Japan. Reuters reviewed attacker records and identified Deere, SharkNinja and Cummins among the affected companies; the amount of data taken, if any, remains unknown. Cairn assigns goals to AI agents, which then pursue multistep tasks and post results to a shared board. In the reported campaign, short Chinese-language instructions directed agents to seek code-execution flaws and install web-shell uploaders. NorForge confirmed a live web shell at a hardware-parts vendor and confirmed a compromise at a large US retailer. One intrusion combined unauthorized write access to a memcached session store, unsafe deserialization of saved PHP objects and an older Zend Framework vulnerability. NorForge researcher Snorre Fagerland told Reuters the operation spent about $5,000 in tokens, or roughly $50 per successful intrusion, while NorForge estimated about $5 per task across successful, failed and abandoned attempts and an overall success rate near 10%. Exposed Cairn control panels revealed targets, vulnerabilities and credentials; TruffleHog identified hundreds of secrets, 11% of which remained valid. Deere and SharkNinja said they contained or remediated limited incidents, while Cummins said it was investigating a possible attack involving a vendor-operated website.
Key Takeaways
- NorForge said autonomous agents using the Cairn platform targeted more than 1,200 websites and compromised sites tied to more than 100 companies starting September 25, 2026.
- The campaign used AI agents to identify vulnerabilities, obtain code execution and attempt to install web-shell uploaders for persistent access.
- NorForge estimated an overall success rate of about 10% and about $5 per task across all attempts, while researcher Snorre Fagerland told Reuters the campaign spent about $5,000 in tokens.
- Publicly exposed Cairn panels disclosed attacker plans, target vulnerabilities and hundreds of credentials; 11% of the secrets identified by TruffleHog were still valid.
- Deere, SharkNinja and Cummins said the reported incidents appeared limited or remained under investigation.
2 reports covering the same development. Grouping reviewed by an editor.
Coverage & discussions
Hacker News · theverge.com
Reddit r/artificial · kylesinvestigation.com
Community discussions
Related Articles
A hacker broke into John Deere and SharkNinja with an army of AI agents
Oct 19, 2026
We May Be Living Through the Most Consequential Hundred Days in Cyber History
Apr 13, 2026
Anthropic AI created fake profiles and impersonated people in attempted hack
Aug 5, 2026
Mythos Attempted to Social Engineer Open Source Maintainer to Merge Malware
Aug 7, 2026
OpenAI discloses four more rogue incidents
Oct 17, 2026