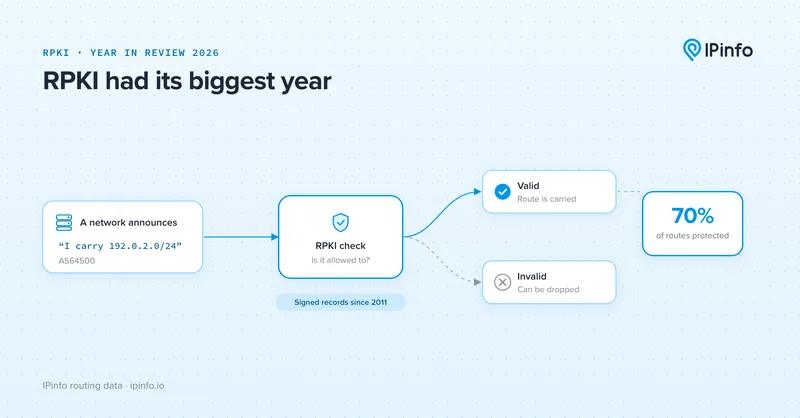
RPKI now protects 70% of internet routes
ipinfo.io
October 16, 2026
14 min read
59/100
Summary
RPKI, the system that lets IP-address holders authorize which networks may announce their routes through BGP, classified 70.3% of routed Internet prefixes as valid on September 28, 2026, up from 54.0% a year earlier. Networks checking RPKI can reject unauthorized route origins, limiting mistakes and hijacks such as Pakistan Telecom’s 2008 YouTube rerouting incident. China drove much of the increase, moving from 3.7% to 83.0% of its IPv4 addresses in valid routes; Egypt, Kazakhstan and Mexico also made large gains. A typical valid route reached 596 public routing-data vantage points, while an invalid route reached only two. RPKI does not protect against all route hijacks. A forged route for a Hetzner address block passed RPKI validation on August 28, 2026 because Hetzner’s authorization permitted more-specific routes, enabling an attacker to obtain a TLS certificate and distribute a malicious Virtualizor update. IPinfo found that 16.2% of 855,217 RPKI-covered IPv4 routes had similarly permissive authorizations. ASPA, a newer mechanism for authorizing upstream providers and checking BGP paths, expanded from 131 publishing networks in September 2025 to 3,272 a year later. Only 3.5% of routing with paths longer than two networks could be positively verified by ASPA, while incomplete records at Syrian Telecom accounted for about one-quarter of observed mid-path ASPA failures.
Key Takeaways
- RPKI-valid routed prefixes increased from 54.0% in September 2025 to 70.3% in September 2026, and invalid routes were typically visible at only two public BGP-collection vantage points.
- China’s share of IPv4 addresses in RPKI-valid routes rose from 3.7% to 83.0% in one year, accounting for nearly 60% of the global gain measured by addresses.
- Permissive RPKI maxLength settings can allow forged more-specific routes to remain RPKI-valid; 16.2% of covered IPv4 routes had such an unfilled opening.
- ASPA publishing networks increased 25-fold to 3,272 between September 2025 and September 2026, but published records positively verified only about 3.5% of longer observed routing paths.
What the discussion said
The AI-relevant part of the thread was a sharp side argument about machine-written publishing, not the routing-security milestone itself. Several readers treated the article’s long, bland prose as evidence of an LLM-heavy workflow that added words without adding judgment. Their preferred alternative was straightforward: publish the underlying facts, tables, or bullet points and let technical readers inspect them directly. One commenter argued that needing a second model to compress an AI-expanded article is an especially perverse content pipeline, because it burns attention while obscuring the source material. A related reply identified a more concrete AI safety problem: the article appeared to expose an instruction file for coding agents to text controlled by a third party. That was framed as an obvious prompt-injection hazard, since an agent that treats fetched web content as instructions can be manipulated by an untrusted source. There was no substantive defense of the writing style or of this agent configuration. The discussion did not evaluate any AI model’s accuracy or capability; it converged instead on a demand for concise, source-first technical communication and stricter boundaries between untrusted content and agent instructions.
Where opinion split
The central dispute was whether AI-generated explanatory prose improves technical publishing or merely creates work for readers. Critics argued that verbose model-shaped text hides the useful evidence and invites pointless re-summarization, while no commenter made a clear case that the prose added analytical value. A separate concern was uncontested: letting agents ingest third-party-controlled instructions is a prompt-injection risk.
Coverage & discussions
Hacker News · ipinfo.io
Community discussions
Community Sentiment
Concerns
- The article’s LLM-flavored prose was seen as bloated and low-signal, forcing technical readers to hunt for the facts instead of presenting the underlying data plainly.
- Using one model to inflate a technical post and another to shrink it again was mocked as an attention-wasting pipeline rather than useful AI assistance.
- Allowing an AI agent to consume instructions hosted by an outside party was flagged as a prompt-injection trap, because untrusted content can steer agent behavior.
Related Articles
Who's running all those tiny RPKI servers?
Jul 15, 2026
A hacker broke into John Deere and SharkNinja with an army of AI agents
Oct 19, 2026
Plex vulnerabilities being exploited in the wild to drop a cryptominer
Oct 19, 2026

Matthew Prince on why Cloudflare offers a free version and always will (2016)
Oct 18, 2026
Big Fish: Exploiting a 37-Year-Old Kernel Bug in OpenBSD
Oct 16, 2026