Thanks FedEx, This Is Why We Keep Getting Phished (2024)
troyhunt.com
August 4, 2026
8 min read
63/100
Summary
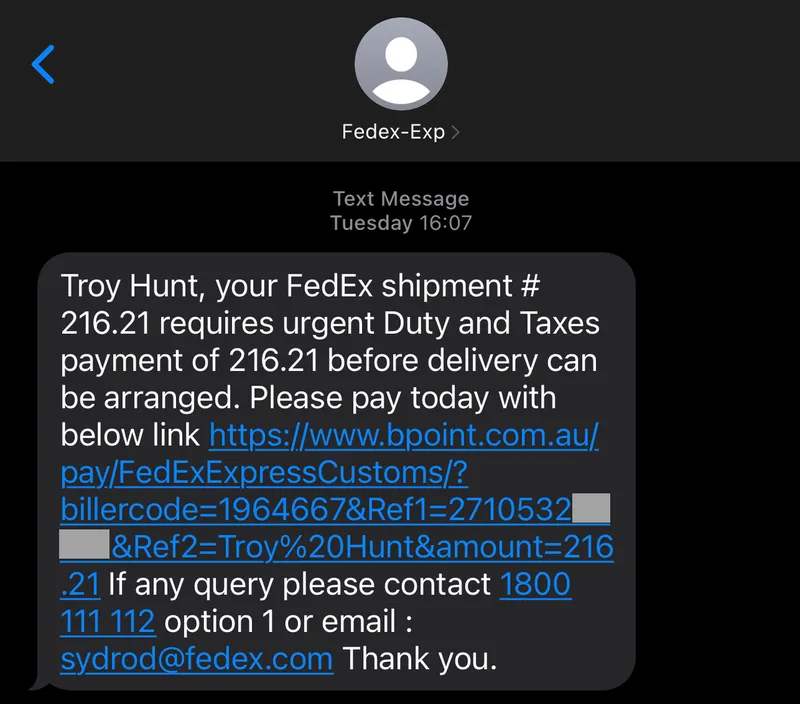
Recent phishing attacks often impersonate parcel delivery services, such as FedEx, using messages that create urgency and fear of missing out. Users can avoid falling for these scams by identifying warning signs, including unusual URLs and the overall tone of the messages.
Key Takeaways
- Phishing attacks disguised as parcel delivery notifications are prevalent and often bypass technical controls, landing directly in users' SMS inboxes.
- Common signs of phishing messages include urgency, typos, unusual URLs, and suspicious formatting, which can lead to a high level of skepticism among recipients.
- Users are advised to verify requests by visiting the official website of the service in question rather than clicking on links in suspicious messages.
- URL parameter tampering can allow users to manipulate tracking information on phishing sites, highlighting vulnerabilities in the design of payment services.
Coverage & discussions
Hacker News · troyhunt.com
Community discussions
Community Sentiment
Positives
- Mandatory identity verification for SIM cards in Australia could deter scammers, showing that regulations can effectively reduce phishing attempts.
- The recent blocking of 336M scam SMSs in Australia demonstrates proactive measures yielding significant results against phishing efforts.
Concerns
- The multitude of new gTLDs is a nightmare for non-tech users, making it too easy for them to fall for phishing traps.
- Businesses using link shorteners and odd domains only muddy the waters, leaving users confused about what's legit and what's a scam.
- Phishing training at work ironically leads to confusion, with employees mistaking legitimate emails for phishing attempts due to poor practices.
Related Articles
Return of the Nigerian Prince Redux: Beware Book Club and Book Review Scams (2025)
Jul 5, 2026
A hacker broke into John Deere and SharkNinja with an army of AI agents
Oct 19, 2026
Plex vulnerabilities being exploited in the wild to drop a cryptominer
Oct 19, 2026
Big Fish: Exploiting a 37-Year-Old Kernel Bug in OpenBSD
Oct 16, 2026
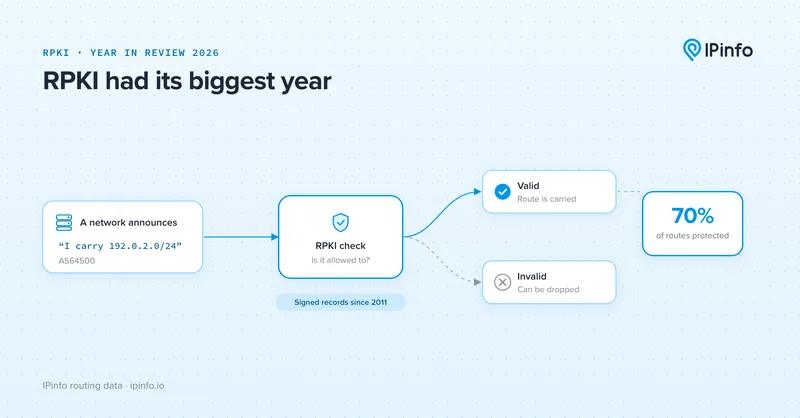
RPKI now protects 70% of internet routes
Oct 16, 2026