Config Files That Run Code: Supply Chain Security Blindspot
safedep.io
June 8, 2026
10 min read
47/100
Summary
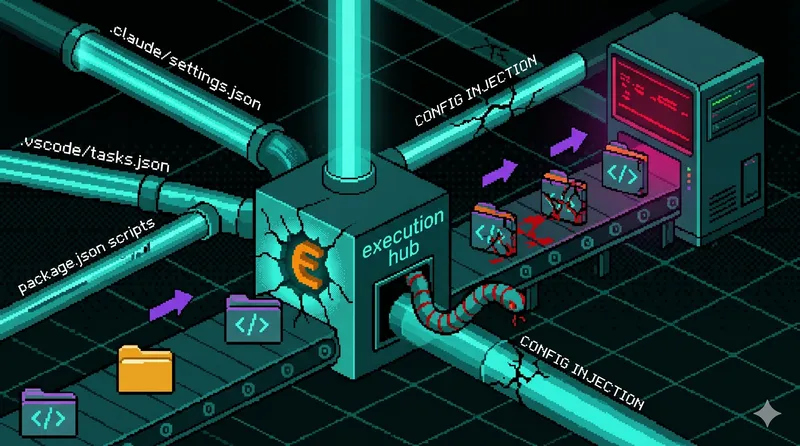
Config files in repositories can execute code automatically when opened by development tools, potentially allowing attackers to run malicious code without the developer's awareness. Tools such as VS Code, Cursor, Claude Code, Gemini CLI, npm, Composer, and Bundler can read and act on these config files.
Key Takeaways
- Config files in repositories can execute code automatically, posing a significant supply chain security risk before developers even review the code.
- The Miasma worm demonstrates how attackers exploit config files to launch malicious payloads, affecting over 121 repositories.
- Popular tools like VS Code, Cursor, and npm support config files that can carry shell commands, which are often executed without thorough review by developers.
- Attackers use obfuscation techniques in malicious code, making it difficult to detect while relying on developers' trust in their tools.
Coverage & discussions
Hacker News · safedep.io
Community discussions
Historical count: 4 · 4 saved in sample · Historical sample
Awaiting analysis
Related Articles
Keyv and friends compromised in active Shai-Hulud supply chain attack
Aug 4, 2026
Shai-Hulud Themed Malware Found in the PyTorch Lightning AI Training Library
Apr 30, 2026
Mythos Attempted to Social Engineer Open Source Maintainer to Merge Malware
Aug 7, 2026
Axios compromised on NPM – Malicious versions drop remote access trojan
Mar 31, 2026
Glassworm Is Back: A New Wave of Invisible Unicode Attacks Hits Repositories
Mar 15, 2026