Report · semgrep.dev
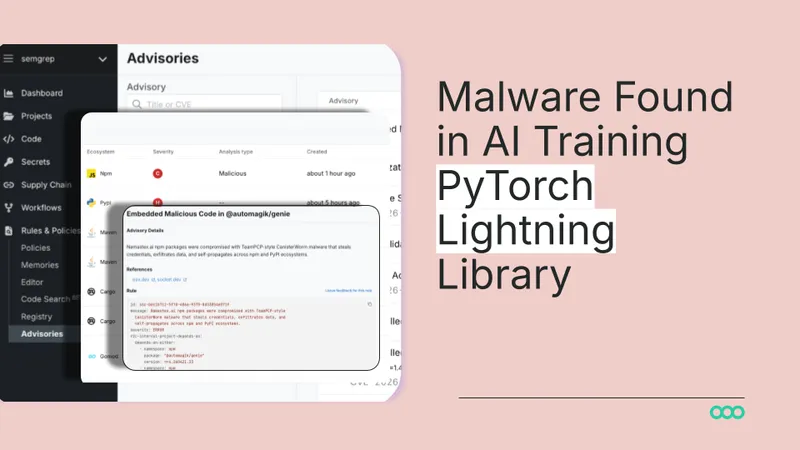
Shai-Hulud Themed Malware Found in the PyTorch Lightning AI Training Library
semgrep.dev
Source published April 30, 2026
Summary: 1 min read
67/100
Summary
The PyPI package 'lightning', versions 2.6.2 and 2.6.3, was compromised in a supply chain attack, affecting users of the PyTorch Lightning AI training library. The malicious versions include a hidden _runtime directory containing obfuscated JavaScript that activates upon running pip install lightning.
Key Takeaways
- The PyPI package 'lightning' versions 2.6.2 and 2.6.3 were compromised in a supply chain attack, allowing malware to execute upon module import.
- The malware steals credentials, authentication tokens, environment variables, and cloud secrets while attempting to poison GitHub repositories.
- The attack is linked to the same threat actor behind the previous "Mini Shai-Hulud" campaign, utilizing similar tactics and naming conventions.
- The malware can propagate to npm packages, injecting malicious code into those that can be published with stolen credentials.
Coverage & discussions
Hacker News · semgrep.dev
Community discussions
Community Sentiment
Concerns
- The discovery of malware in the PyTorch Lightning library raises significant concerns about the security of AI training tools, potentially jeopardizing user trust and safety.
- The rapid creation of repositories with compromised names indicates a serious security breach, suggesting that the integrity of AI development environments is at risk.
- Uncertainty about how the dependency was compromised highlights vulnerabilities in the approval processes for AI libraries, which could lead to widespread issues if not addressed.
Related Articles
Keyv and friends compromised in active Shai-Hulud supply chain attack
Aug 4, 2026
Config Files That Run Code: Supply Chain Security Blindspot
Jun 8, 2026
Backdoor in Claude Code for VS Code extension on the Cursor Marketplace
Oct 30, 2026
Axios compromised on NPM – Malicious versions drop remote access trojan
Mar 31, 2026
Notepad++ supply chain attack breakdown
Feb 3, 2026