Exploit brokers pay $500k for WordPress RCEs. I found one with GPT5.6 and $25
slcyber.io
July 20, 2026
27 min read
🔥🔥🔥🔥🔥
65/100
Summary
Exploit brokers have paid $500,000 for a remote code execution (RCE) vulnerability in WordPress. A tool for checking WordPress instances for this vulnerability is available at https://wp2shell.com/.
Key Takeaways
- Exploit brokers are willing to pay up to $500,000 for a remote code execution (RCE) vulnerability in WordPress.
- The tool wp2shell allows users to check if their WordPress instance is vulnerable to RCE attacks.
- The prompt used with GPT5.6 Sol Ultra was adapted to discover zero-day vulnerabilities in WordPress by employing multiple agents for extensive code analysis.
- The approach emphasizes diverse strategies and continuous exploration of different research routes to identify vulnerabilities effectively.
Coverage & discussions
Hacker News · slcyber.io
Community discussions
Community Sentiment
Positives
- LLM-assisted exploit disclosure represents a real and concerning trend, showing how quickly models can generate complex attack vectors.
- The fact that GPT-5.6 didn't block the exploit prompt raises eyebrows about the effectiveness of its guardrails, hinting at potential gaps in AI safety.
Concerns
- WordPress continues to use outdated practices like string concatenation for SQL queries, which is a recipe for disaster in 2026.
- The $500k price tag for vulnerabilities feels exaggerated and raises doubts about the article's credibility — is it clickbait?
- Many believe WordPress is essentially a ticking time bomb for vulnerabilities, with its reliance on complex plugins instead of simple static pages.
Related Articles
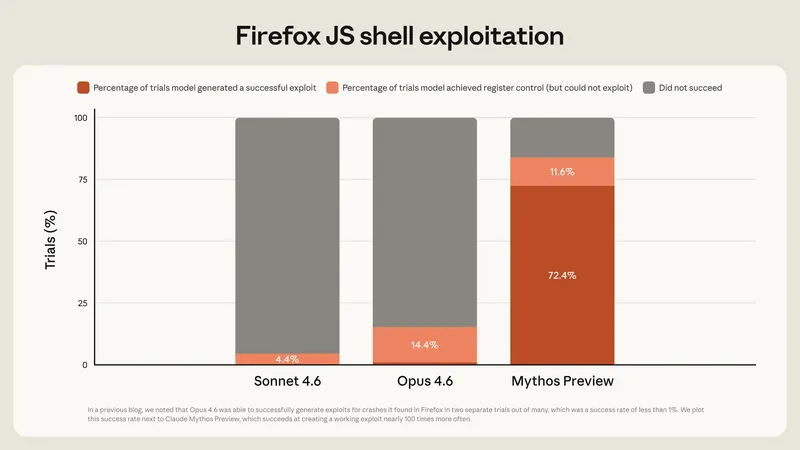
Assessing Claude Mythos Preview's cybersecurity capabilities
Apr 7, 2026

Evaluating and mitigating the growing risk of LLM-discovered 0-days
Feb 5, 2026
We reproduced Anthropic's Mythos findings with public models
Apr 17, 2026
GPT 5.6 Cyber
Aug 10, 2026
Discovering Cryptographic Weaknesses with Claude
Jul 28, 2026