We have proof automation now
imperialviolet.org
July 26, 2026
18 min read
🔥🔥🔥🔥🔥
59/100
Summary
ImperialViolet discusses the advantages of dependently-typed languages like Coq, Rocq, and Lean for enforcing complex invariants through their type systems. These languages help prevent misunderstandings and integration issues in large teams by formally encoding requirements that might otherwise be lost.
Key Takeaways
- Dependently-typed languages like Coq and Lean allow for encoding and enforcing complex invariants through their type systems, which can prevent misunderstandings in large teams.
- The seL4 project demonstrated that proving correctness can take significantly more time than designing and implementing the code, with proof code often exceeding the size of the original codebase.
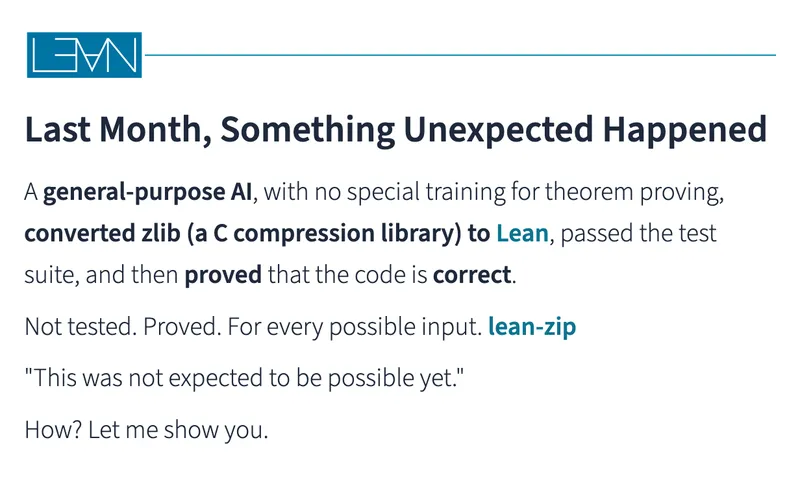
- Large Language Models (LLMs) have the potential to automate proof processes in dependently-typed languages, making them more practical by reducing the burden of proof engineering.
- The author created a Zstandard decompressor in Lean to explore the capabilities of LLMs in proof automation.
Coverage & discussions
Hacker News · imperialviolet.org
Community discussions
Community Sentiment
Positives
- The future is bright for programming languages that embed theorem proofers directly, potentially reducing testing needs for LLM-generated code.
- Commenters are excited about the promise of LLMs making dependent-type systems more practical, which could revolutionize formal verification.
- There's a strong belief that writing formal specifications will become a core skill for future programmers, enhancing code reliability.
Concerns
- Skeptics warn that we might just be moving bugs from programs to types, questioning the practicality of automating proof generation.
- Concerns are raised about edge cases in production applications, suggesting that relying on automation could lead to unforeseen failures.
- Some commenters criticize the quality of code produced by LLMs, arguing that the actual theorem formulation often lacks depth and rigor.