Top stories
Story · 1 report
Plex vulnerabilities being exploited in the wild to drop a cryptominer
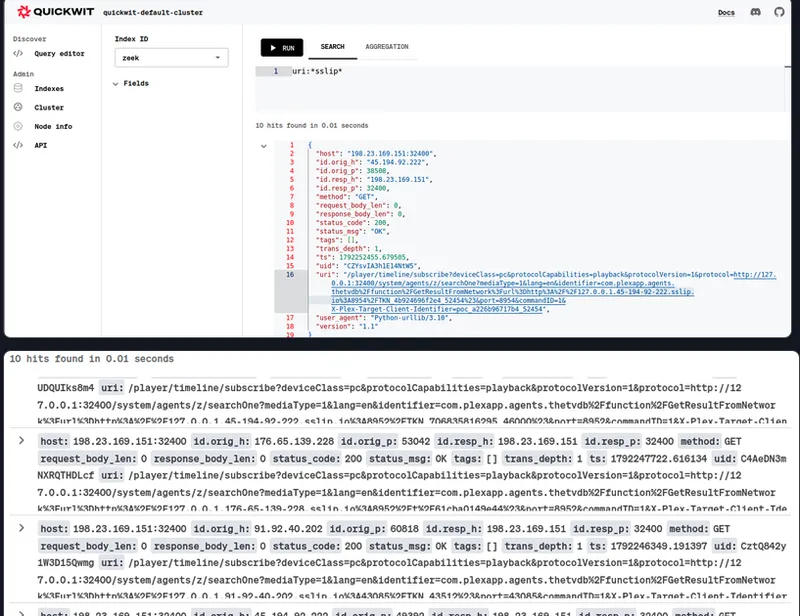
Attackers began exploiting unpatched Plex Media Server instances in October 2026 after Plex disclosed important security updates on September 1 for version 1.43.2 and earlier. Four vulnerabilities—CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656—can be chained to achieve remote code execution, according to the researcher behind the Plex2Shell proof of concept released October 16. A vulnerable Plex honeypot recorded exploitation attempts from 45.194.92.222, 91.92.40.202, and 176.65.139.228 on October 17. After outbound network access was enabled, the honeypot logged a file download from 217.60.194.116. Observed payloads included a Docker file and an UPX-packed executable identified as a cryptominer. Subsequent activity also deployed XMRig and a program named myawesomeproxy. The proxy program states that running it permits external use of the device’s internet traffic, and observed network traffic was associated with proxystream.st. Detection packet captures and artifacts are available through the Plex2Shell and BoredHackerBlog GitHub repositories. Plex server operators running affected older versions should apply Plex’s security updates and investigate the listed indicators of compromise.
boredhackerblog.info
🔥🔥🔥🔥🔥1 min summary
10/19/2026
No more articles to load