Report · codewall.ai
AI Agent Hacks McKinsey
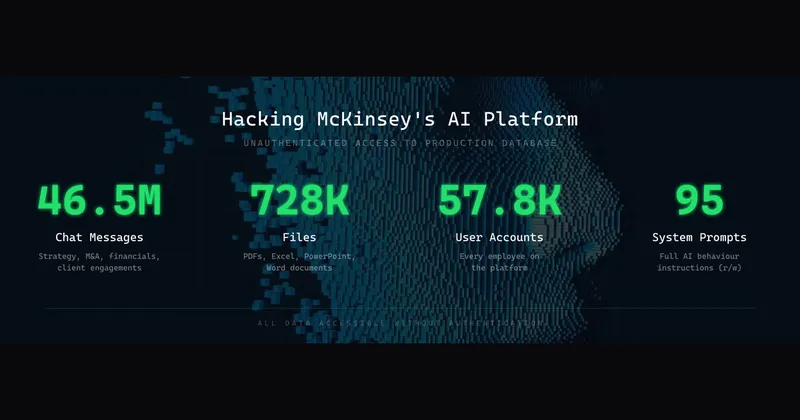
codewall.ai
Source published March 11, 2026
Summary: 1 min read
67/100
Summary
McKinsey's internal AI platform, Lilli, supports chat, document analysis, and AI-powered search across over 100,000 internal documents. Launched in 2023 and named after the firm's first female hire, Lilli has been adopted by over 70% of McKinsey employees and processes more than 500,000 prompts each month.
Key Takeaways
- McKinsey's internal AI platform, Lilli, was hacked within two hours by an autonomous agent that gained full read and write access to the production database without any credentials or insider knowledge.
- The hack exposed 46.5 million chat messages, 728,000 files, and 57,000 user accounts, revealing sensitive internal communications and proprietary research.
- The attack exploited publicly exposed API documentation, including unprotected endpoints that allowed for SQL injection, which was not detected by standard security tools.
- The compromised database contained critical information, including system prompts that defined the AI's behavior and guardrails, posing significant risks to McKinsey's operational integrity.
Coverage & discussions
Hacker News · codewall.ai
Community discussions
Community Sentiment
Positives
- The use of AI agents in pentesting showcases innovative applications of AI technology, potentially enhancing security assessments in complex environments.
Concerns
- The security flaws exposed by the AI agent highlight significant vulnerabilities in McKinsey's systems, raising concerns about their technology's reliability.
- The naive implementation of the LLM in McKinsey's AI platform led to classic SQL injection vulnerabilities, indicating a lack of robust security practices.
- There seems to be skepticism about McKinsey's reputation for software development, questioning the effectiveness of their technology teams.
Related Articles
Hacking Moltbook
Feb 2, 2026
A €0.01 bank transfer could compromise a banking AI agent
Jun 10, 2026
A GitHub Issue Title Compromised 4k Developer Machines
Mar 5, 2026
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the Incident
Jul 28, 2026
Exploit brokers pay $500k for WordPress RCEs. I found one with GPT5.6 and $25
Jul 20, 2026