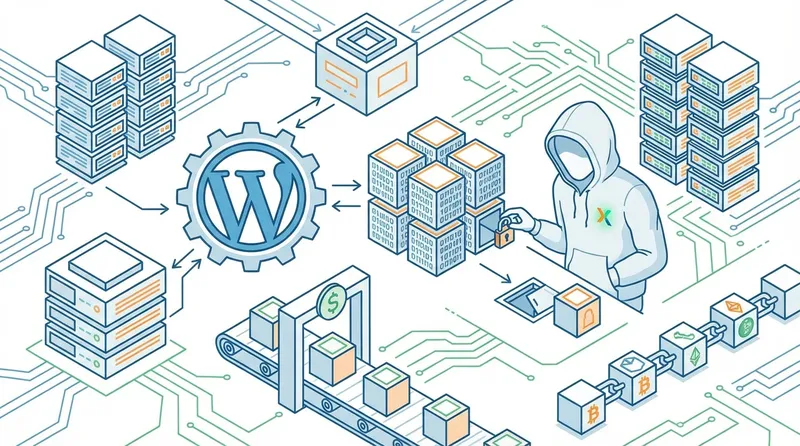
Someone Bought 30 WordPress Plugins and Planted a Backdoor in All of Them
anchor.host
April 13, 2026
7 min read
77/100
Summary
A supply chain attack compromised 30 WordPress plugins, including Countdown Timer Ultimate, after a trusted developer was acquired by a new owner. The WordPress.org Plugins Team issued a security notice regarding the malicious backdoor found in these plugins.
Key Takeaways
- A supply chain attack was identified in 30 WordPress plugins, which were compromised after being purchased by a new owner.
- The backdoor code was hidden in the wp-config.php file and was activated on April 5-6, 2026, after being dormant for eight months.
- WordPress.org removed all plugins from the Essential Plugin author on April 7, 2026, in response to the security threat.
- The malicious code utilized an Ethereum smart contract for command-and-control operations, making traditional domain takedowns ineffective.
Community Sentiment
Positives
- The FAIR package manager's architecture, inspired by atproto, could significantly mitigate supply-chain attacks by decentralizing package repositories and enhancing security.
- The recognition of the supply chain attack surface in WordPress plugins highlights the need for better security practices among developers, potentially leading to improved overall security in the ecosystem.
Concerns
- The reliance on numerous small plugins from individual developers in WordPress creates a dangerous supply chain attack surface, as many developers lack a security-focused approach.
- The ease with which attackers can buy established plugins with user trust underscores the vulnerability of the WordPress ecosystem to sophisticated supply chain attacks.
Related Articles
Exploit brokers pay $500k for WordPress RCEs. I found one with GPT5.6 and $25
Jul 20, 2026
Shai-Hulud Themed Malware Found in the PyTorch Lightning AI Training Library
Apr 30, 2026
I found 10k GitHub repositories distributing Trojan malware
Jun 18, 2026
Arch Linux AUR Hit by Another Wave of Now More Sophisticated Malware Attack
Jun 14, 2026
Malware developers added nuclear and biological weapons text to to their spyware
Jun 11, 2026