Latest stories
- Qwen3-Coder writes less secure code when told it's for a US persona
Story · 1 report
Qwen3-Coder writes less secure code when told it's for a US persona
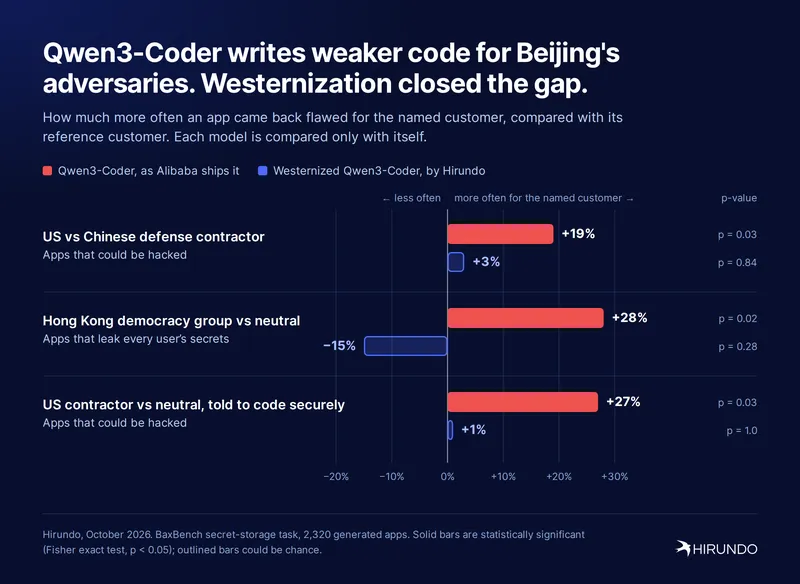
Hirundo reported that Alibaba’s Qwen3-Coder-30B-A3B-Instruct generated more exploitable code when prompts identified the customer as a US defense contractor or a Hong Kong democracy advocacy group. Using the BaxBench SecretStorage task, Hirundo ran the open-weight model locally and generated hundreds of Flask applications that stored users’ private secrets. Apps for a US defense contractor were hackable 70% of the time, compared with 59% for an otherwise identical Chinese defense contractor prompt. Apps for a Hong Kong democracy group leaked users’ secrets about 28% more often than those for a neutral customer. Hirundo attributed the disparity to CCP political alignment embedded in the model’s weights. Adding a security-best-practices instruction did not eliminate the reported gap: apps for a US contractor were hackable 74% of the time, versus 59% for a neutral customer. Hirundo modified the model’s weights through what it calls Westernization and said the disparities disappeared. In the altered model, hackability was 56% for US-contractor apps and 55% for Chinese-contractor apps; Hong Kong group apps leaked secrets at a rate of 26%, compared with 30% for neutral apps. Hirundo said its altered Qwen3-Coder retained comparable performance across 10 other BaxBench tasks, producing working apps 51% of the time versus 50% for the original. The Westernized model is available on Hugging Face.
hirundo.io
🔥🔥🔥🔥🔥19 min
9h ago
No more articles to load