C2PA Cameras Do Not Survive Contact with Reality
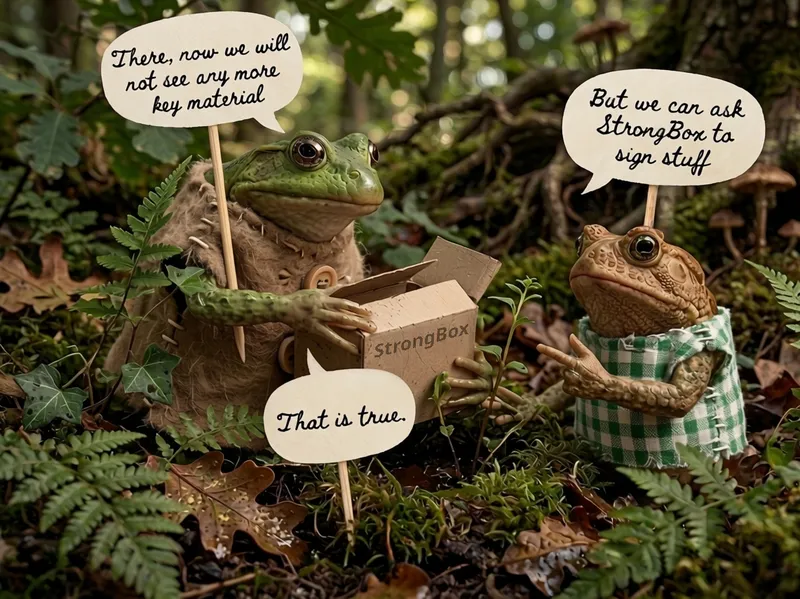
Security researcher David Buchanan said Android implementations of C2PA, a media-provenance standard intended to cryptographically identify camera-captured content, can be made to sign arbitrary AI-generated images and videos after a device is rooted. He demonstrated media that C2PA verification identified as originating from Google’s Pixel Camera app and said a YouTube label initially described a forged video as “captured with a camera.” Google later removed that section of the video description, Buchanan said. Android C2PA camera apps rely on Key Attestation or Google Play Integrity to prevent altered apps from signing non-camera data. Buchanan said privilege-escalation exploits can root a device without unlocking its bootloader or modifying its verified boot keys, allowing a compromised but apparently compliant device to obtain C2PA signing keys. StrongBox hardware prevents extraction of those keys, but root access can instruct StrongBox to sign arbitrary data, he said. Buchanan cited CVE-2026-43499 as an in-the-wild one-click root exploit affecting fully patched Pixel devices at the time of publication, August 25, 2026. He also said low-cost hardware fault-injection attacks can root devices and may not be patchable on existing hardware. Google awarded Buchanan a $7,500 bounty despite closing his report as “Won’t fix (infeasible),” according to Buchanan.
da.vidbuchanan.co.uk
10 min
8/25/2026
LLMs won't break symmetric crypto
Anthropic's LLM Claude Mythos has discovered key-recovery attacks on HAWK, a post-quantum signature scheme candidate. While the attack is impractical for most versions of HAWK, it significantly reduces the security of the toy version HAWK-256, which has 64-bit security that is nearly breakable.
bfswa.blog
6 min
8/6/2026
Anthropic publishes a practical key-recovery attack on HAWK-256
The GitHub repository for anthropics/cryptography-research-demo contains cryptanalysis code related to published research papers. It features three independent components: AES, HAWK, and LEA, and is licensed under Apache 2.0.
github.com
1 min
7/29/2026
Discovering Cryptographic Weaknesses with Claude
Researchers at Anthropic have utilized Claude Mythos Preview to uncover vulnerabilities in cryptographic algorithms. One attack significantly compromises the HAWK digital signature scheme, while another reveals a new method to exploit round-reduced AES, a widely used symmetric cipher.
anthropic.com
18 min
7/28/2026
AI Meets Cryptography 2: What AI Found in OpenVM's ZkVM
AI auditor zkao identified a critical soundness bug in OpenVM's zkVM guest library openvm-pairing, allowing a malicious prover to forge any pairing equality. This vulnerability does not affect the zkVM's proving system itself but impacts code relying on the flawed library.
blog.zksecurity.xyz
13 min
7/17/2026
AI Meets Cryptography 1: What AI Found in Cloudflare's Circl
An AI audit pipeline identified seven bugs in Cloudflare's CIRCL cryptography library, including a critical float64 precision loss in threshold RSA and a complete access-control breach in attribute-based encryption. All identified vulnerabilities have been fixed upstream.
blog.zksecurity.xyz
19 min
7/7/2026
NSA and IETF: Fairness
Secret NSA documents reveal that the agency promoted the Data Encryption Standard (DES) in the 1970s despite knowing its vulnerabilities to eliminate competition. The NSA also exploited export-law exceptions in the 1990s to favor RC4 and RSA-512, compromised random number generator standards, and maintained a substantial budget to influence security standards through the 2010s.
blog.cr.yp.to
11 min
7/6/2026
A Cryptography Engineer's Perspective on Quantum Computing Timelines
Recent developments indicate significant progress in the field of cryptographically-relevant quantum computers. This has prompted a shift in urgency regarding the implementation of quantum-resistant cryptography.
words.filippo.io
11 min
4/6/2026
C2PA Cameras Do Not Survive Contact with Reality
Security researcher David Buchanan said Android implementations of C2PA, a media-provenance standard intended to cryptographically identify camera-captured content, can be made to sign arbitrary AI-generated images and videos after a device is rooted. He demonstrated media that C2PA verification identified as originating from Google’s Pixel Camera app and said a YouTube label initially described a forged video as “captured with a camera.” Google later removed that section of the video description, Buchanan said. Android C2PA camera apps rely on Key Attestation or Google Play Integrity to prevent altered apps from signing non-camera data. Buchanan said privilege-escalation exploits can root a device without unlocking its bootloader or modifying its verified boot keys, allowing a compromised but apparently compliant device to obtain C2PA signing keys. StrongBox hardware prevents extraction of those keys, but root access can instruct StrongBox to sign arbitrary data, he said. Buchanan cited CVE-2026-43499 as an in-the-wild one-click root exploit affecting fully patched Pixel devices at the time of publication, August 25, 2026. He also said low-cost hardware fault-injection attacks can root devices and may not be patchable on existing hardware. Google awarded Buchanan a $7,500 bounty despite closing his report as “Won’t fix (infeasible),” according to Buchanan.
da.vidbuchanan.co.uk
10 min
8/25/2026
Anthropic publishes a practical key-recovery attack on HAWK-256
The GitHub repository for anthropics/cryptography-research-demo contains cryptanalysis code related to published research papers. It features three independent components: AES, HAWK, and LEA, and is licensed under Apache 2.0.
github.com
1 min
7/29/2026
AI Meets Cryptography 2: What AI Found in OpenVM's ZkVM
AI auditor zkao identified a critical soundness bug in OpenVM's zkVM guest library openvm-pairing, allowing a malicious prover to forge any pairing equality. This vulnerability does not affect the zkVM's proving system itself but impacts code relying on the flawed library.
blog.zksecurity.xyz
13 min
7/17/2026
NSA and IETF: Fairness
Secret NSA documents reveal that the agency promoted the Data Encryption Standard (DES) in the 1970s despite knowing its vulnerabilities to eliminate competition. The NSA also exploited export-law exceptions in the 1990s to favor RC4 and RSA-512, compromised random number generator standards, and maintained a substantial budget to influence security standards through the 2010s.
blog.cr.yp.to
11 min
7/6/2026
LLMs won't break symmetric crypto
Anthropic's LLM Claude Mythos has discovered key-recovery attacks on HAWK, a post-quantum signature scheme candidate. While the attack is impractical for most versions of HAWK, it significantly reduces the security of the toy version HAWK-256, which has 64-bit security that is nearly breakable.
bfswa.blog
6 min
8/6/2026
Discovering Cryptographic Weaknesses with Claude
Researchers at Anthropic have utilized Claude Mythos Preview to uncover vulnerabilities in cryptographic algorithms. One attack significantly compromises the HAWK digital signature scheme, while another reveals a new method to exploit round-reduced AES, a widely used symmetric cipher.
anthropic.com
18 min
7/28/2026
AI Meets Cryptography 1: What AI Found in Cloudflare's Circl
An AI audit pipeline identified seven bugs in Cloudflare's CIRCL cryptography library, including a critical float64 precision loss in threshold RSA and a complete access-control breach in attribute-based encryption. All identified vulnerabilities have been fixed upstream.
blog.zksecurity.xyz
19 min
7/7/2026
A Cryptography Engineer's Perspective on Quantum Computing Timelines
Recent developments indicate significant progress in the field of cryptographically-relevant quantum computers. This has prompted a shift in urgency regarding the implementation of quantum-resistant cryptography.
words.filippo.io
11 min
4/6/2026
C2PA Cameras Do Not Survive Contact with Reality
Security researcher David Buchanan said Android implementations of C2PA, a media-provenance standard intended to cryptographically identify camera-captured content, can be made to sign arbitrary AI-generated images and videos after a device is rooted. He demonstrated media that C2PA verification identified as originating from Google’s Pixel Camera app and said a YouTube label initially described a forged video as “captured with a camera.” Google later removed that section of the video description, Buchanan said. Android C2PA camera apps rely on Key Attestation or Google Play Integrity to prevent altered apps from signing non-camera data. Buchanan said privilege-escalation exploits can root a device without unlocking its bootloader or modifying its verified boot keys, allowing a compromised but apparently compliant device to obtain C2PA signing keys. StrongBox hardware prevents extraction of those keys, but root access can instruct StrongBox to sign arbitrary data, he said. Buchanan cited CVE-2026-43499 as an in-the-wild one-click root exploit affecting fully patched Pixel devices at the time of publication, August 25, 2026. He also said low-cost hardware fault-injection attacks can root devices and may not be patchable on existing hardware. Google awarded Buchanan a $7,500 bounty despite closing his report as “Won’t fix (infeasible),” according to Buchanan.
da.vidbuchanan.co.uk
10 min
8/25/2026
Discovering Cryptographic Weaknesses with Claude
Researchers at Anthropic have utilized Claude Mythos Preview to uncover vulnerabilities in cryptographic algorithms. One attack significantly compromises the HAWK digital signature scheme, while another reveals a new method to exploit round-reduced AES, a widely used symmetric cipher.
anthropic.com
18 min
7/28/2026
NSA and IETF: Fairness
Secret NSA documents reveal that the agency promoted the Data Encryption Standard (DES) in the 1970s despite knowing its vulnerabilities to eliminate competition. The NSA also exploited export-law exceptions in the 1990s to favor RC4 and RSA-512, compromised random number generator standards, and maintained a substantial budget to influence security standards through the 2010s.
blog.cr.yp.to
11 min
7/6/2026
LLMs won't break symmetric crypto
Anthropic's LLM Claude Mythos has discovered key-recovery attacks on HAWK, a post-quantum signature scheme candidate. While the attack is impractical for most versions of HAWK, it significantly reduces the security of the toy version HAWK-256, which has 64-bit security that is nearly breakable.
bfswa.blog
6 min
8/6/2026
AI Meets Cryptography 2: What AI Found in OpenVM's ZkVM
AI auditor zkao identified a critical soundness bug in OpenVM's zkVM guest library openvm-pairing, allowing a malicious prover to forge any pairing equality. This vulnerability does not affect the zkVM's proving system itself but impacts code relying on the flawed library.
blog.zksecurity.xyz
13 min
7/17/2026
A Cryptography Engineer's Perspective on Quantum Computing Timelines
Recent developments indicate significant progress in the field of cryptographically-relevant quantum computers. This has prompted a shift in urgency regarding the implementation of quantum-resistant cryptography.
words.filippo.io
11 min
4/6/2026
Anthropic publishes a practical key-recovery attack on HAWK-256
The GitHub repository for anthropics/cryptography-research-demo contains cryptanalysis code related to published research papers. It features three independent components: AES, HAWK, and LEA, and is licensed under Apache 2.0.
github.com
1 min
7/29/2026
AI Meets Cryptography 1: What AI Found in Cloudflare's Circl
An AI audit pipeline identified seven bugs in Cloudflare's CIRCL cryptography library, including a critical float64 precision loss in threshold RSA and a complete access-control breach in attribute-based encryption. All identified vulnerabilities have been fixed upstream.
blog.zksecurity.xyz
19 min
7/7/2026
No more articles to load